
Eliminate Article Distractions with Safari Reader
Tired of ads and pop-ups interrupting your reading? Safari Reader reformats Web articles for distraction-free viewing on the iPhone, iPad, and Mac—and it can even activate automatically.
Reading articles on the Web has become fraught with distraction. Ads are terrible, of course, but publications also inundate you with navigation links, pop-ups encouraging you to subscribe, popular article lists, and more. Even worse is when an article requires multiple clicks or taps to keep reading. It’s maddening—you just want to read and get on with your day!
The easiest, built-in solution to this admittedly first-world problem for Apple users is Safari Reader on the iPhone, iPad, and Mac, which you can use to “hide navigation menus and other distracting items.”
Apple is careful not to say that Reader hides ads—which it does, most of the time—to avoid conflict with publications that rely on advertising, some of which may even be placed by Apple itself.
Beyond hiding distracting items, Reader displays articles as a single page and automatically generates a summary and table of contents for longer articles to make navigation easier.
Even better, you can configure Safari to show articles in Reader automatically for specific websites, so you don’t have to turn it on manually for each article.
Here’s how to use it.
Switch to Reader
Since Reader’s reformatting would break many non-article Web pages, Safari offers Reader only when you’re viewing a page that it can reformat. As a reminder, Safari on the iPhone and iPad shows a brief “Reader Available” mention in the address bar when you open a Reader-compatible page.
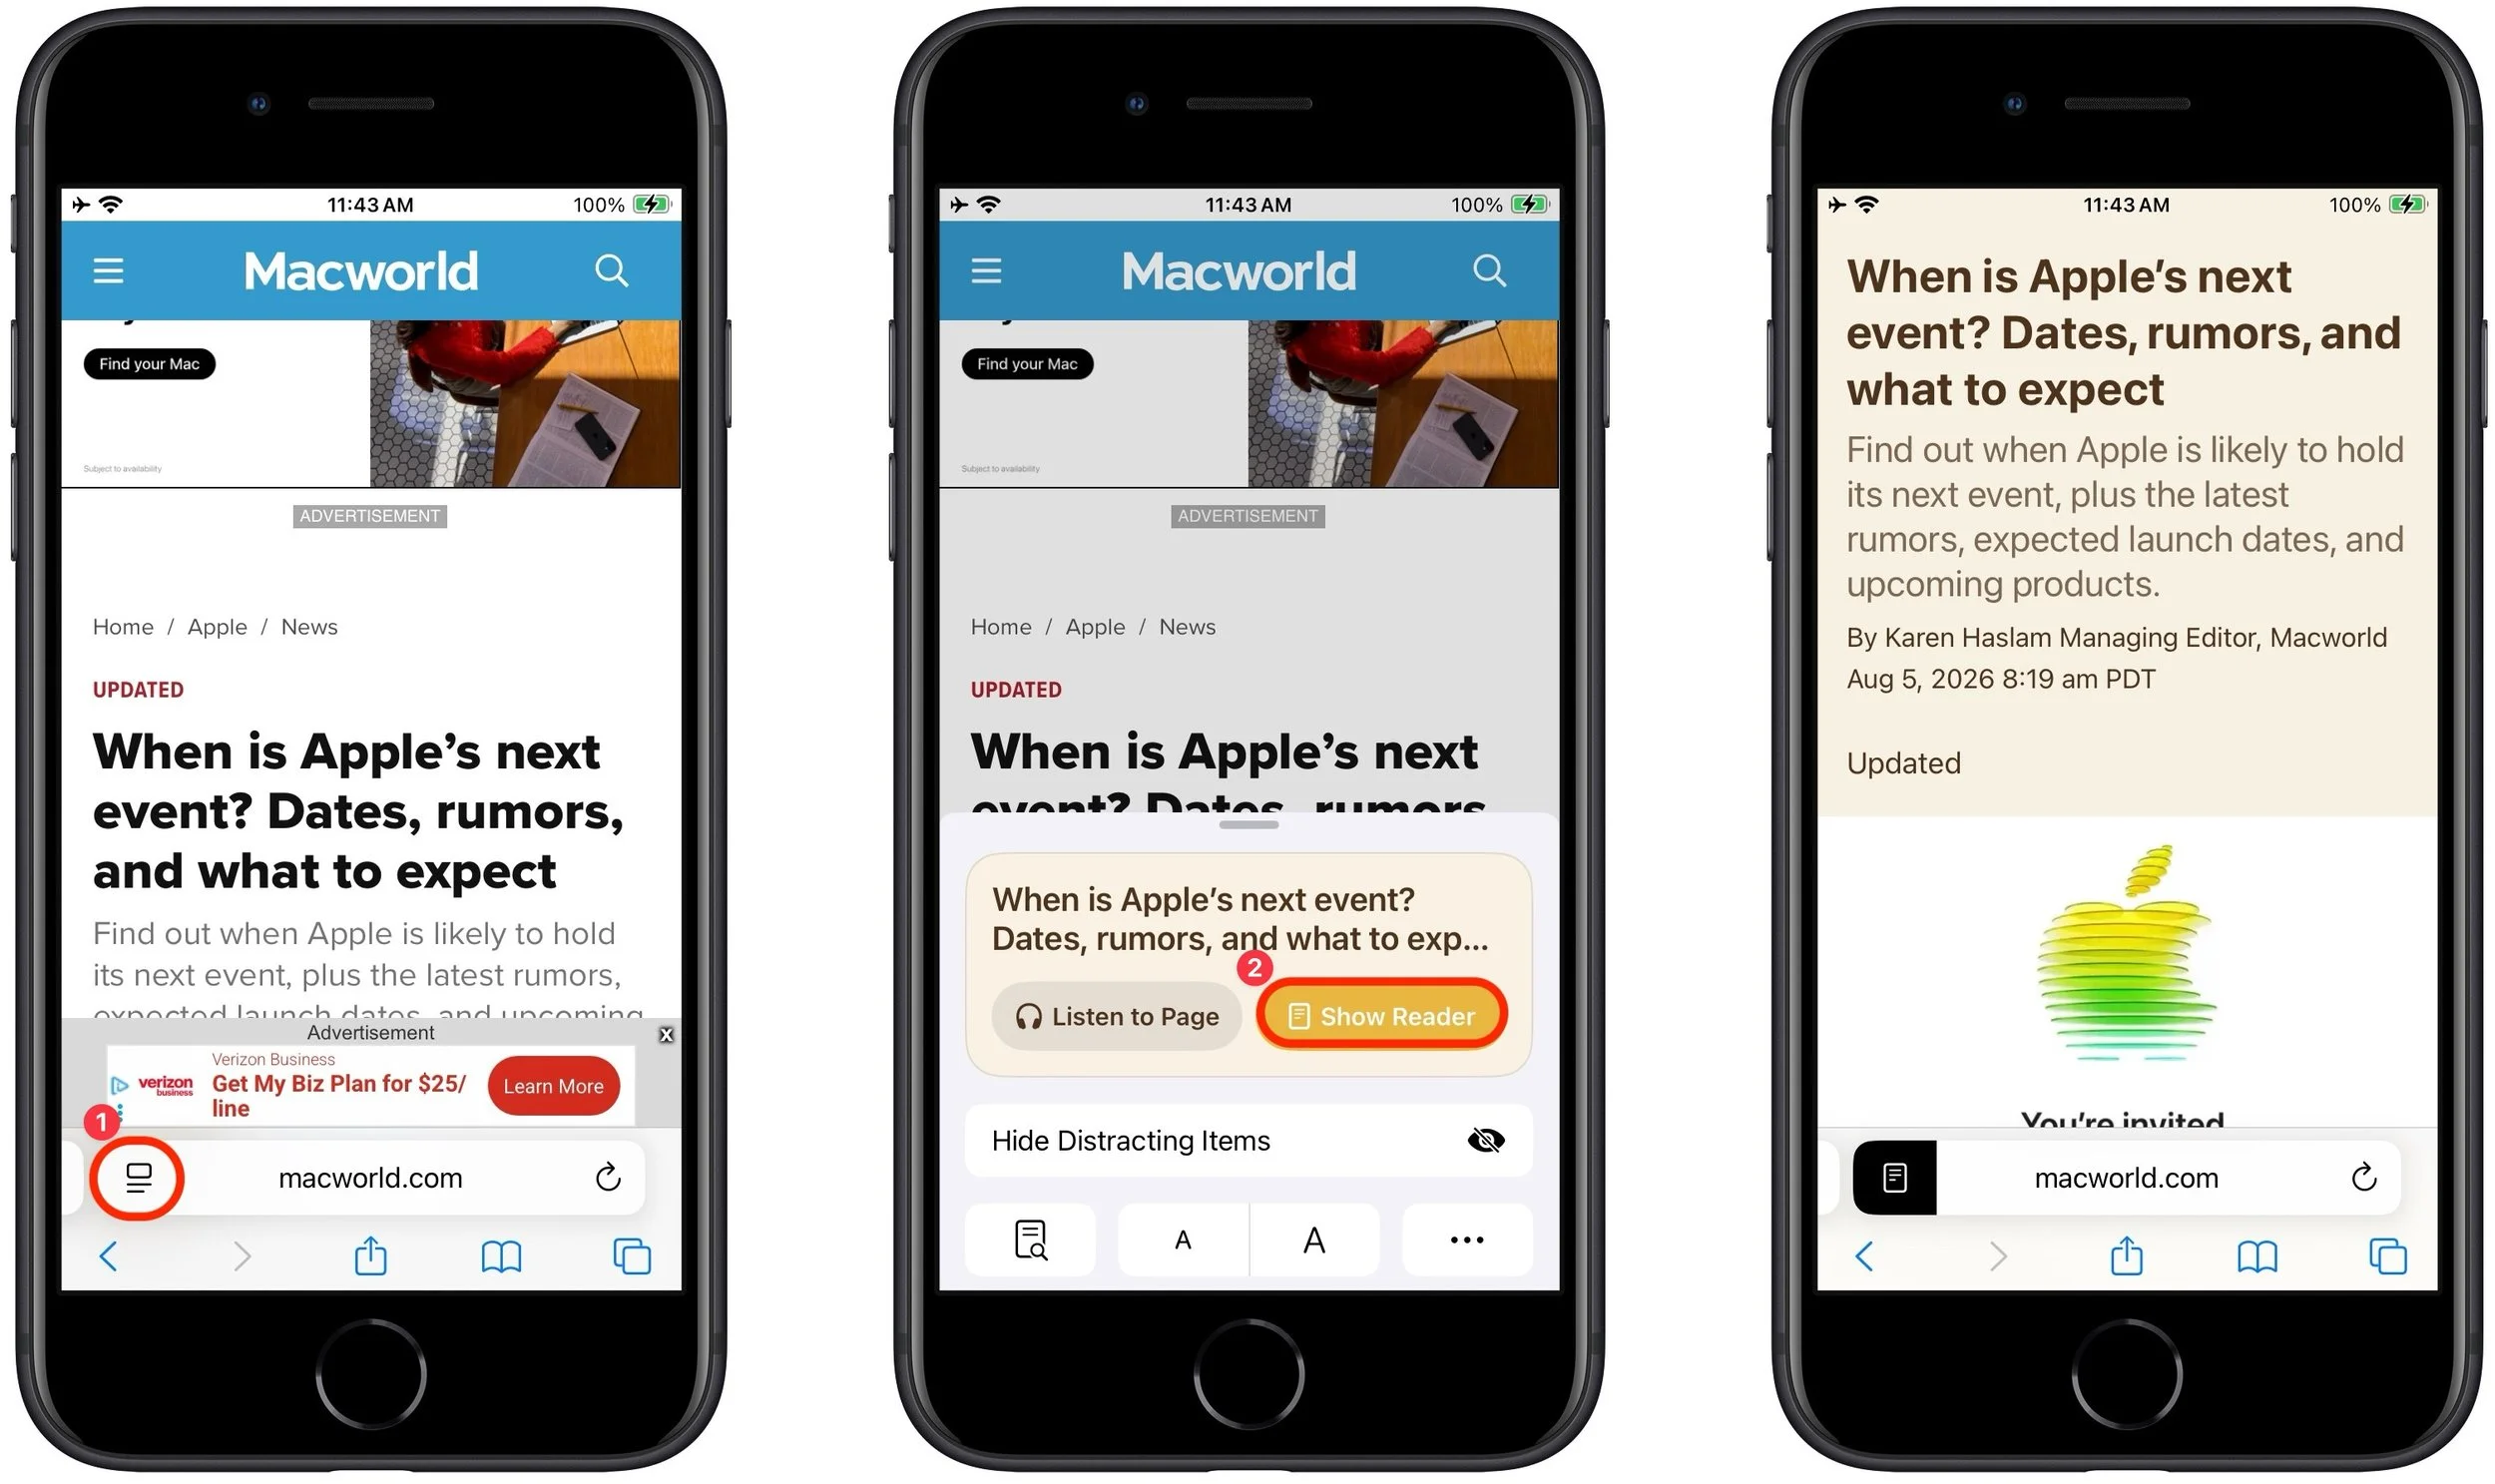
To display a compatible page in Reader, tap the website button at the left of the address bar ➊, then tap Show Reader ➋. Safari immediately reformats the page, removing many extraneous items and potentially changing the background and font.
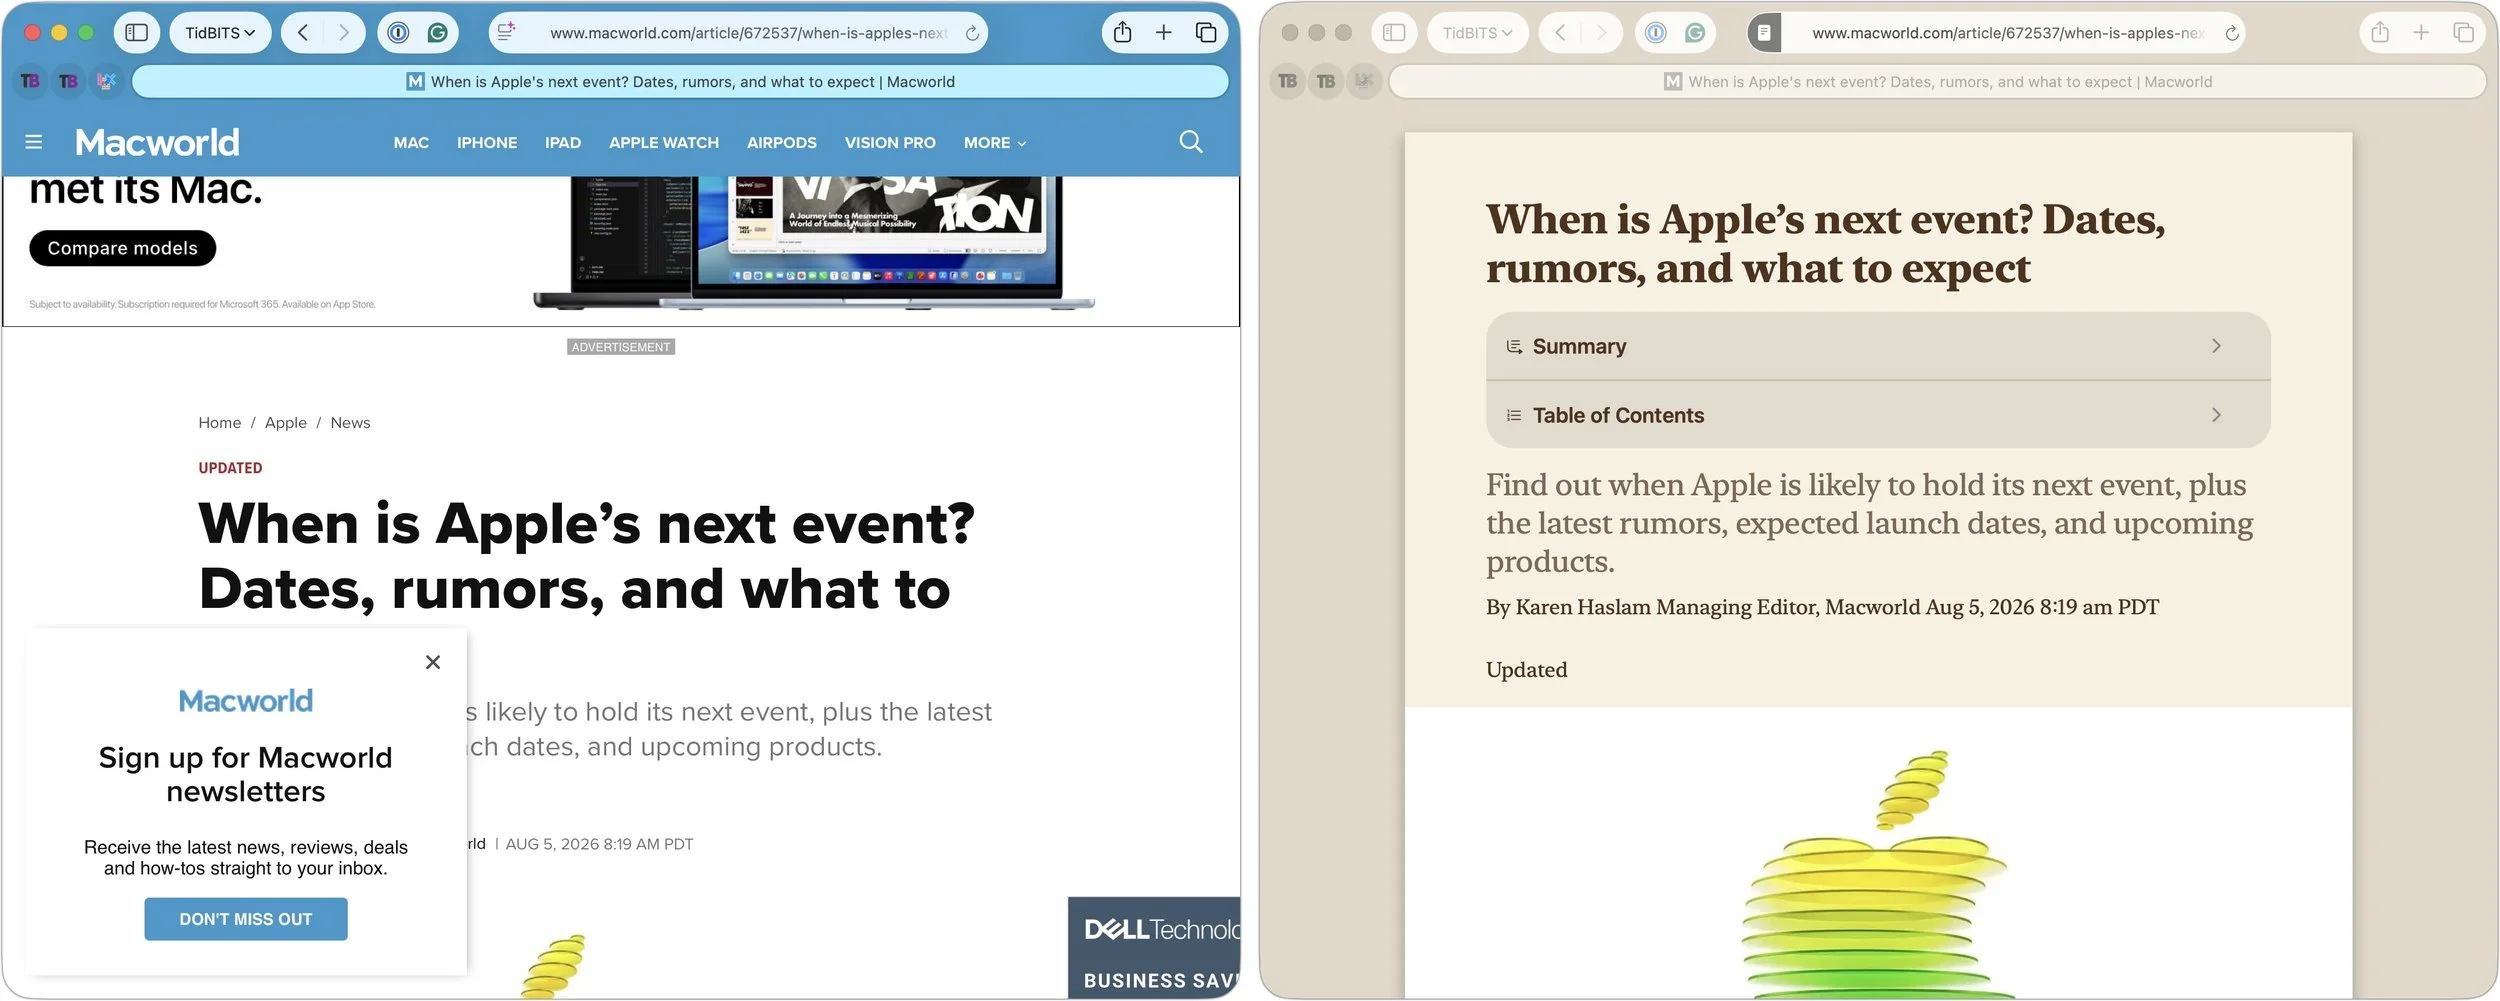
The reformatting can be even more significant in Safari on the Mac, where websites often add columns of ads, pop-ups over the text you want to read, and more.
When Reader decides a page is long enough and has enough headings, it automatically generates a summary and table of contents, displaying them in expandable sections at the top. This feature is, frankly, a little random. We couldn’t always predict when Reader would generate those sections, and it even sometimes varied by device.
Adjust the Look of Reader
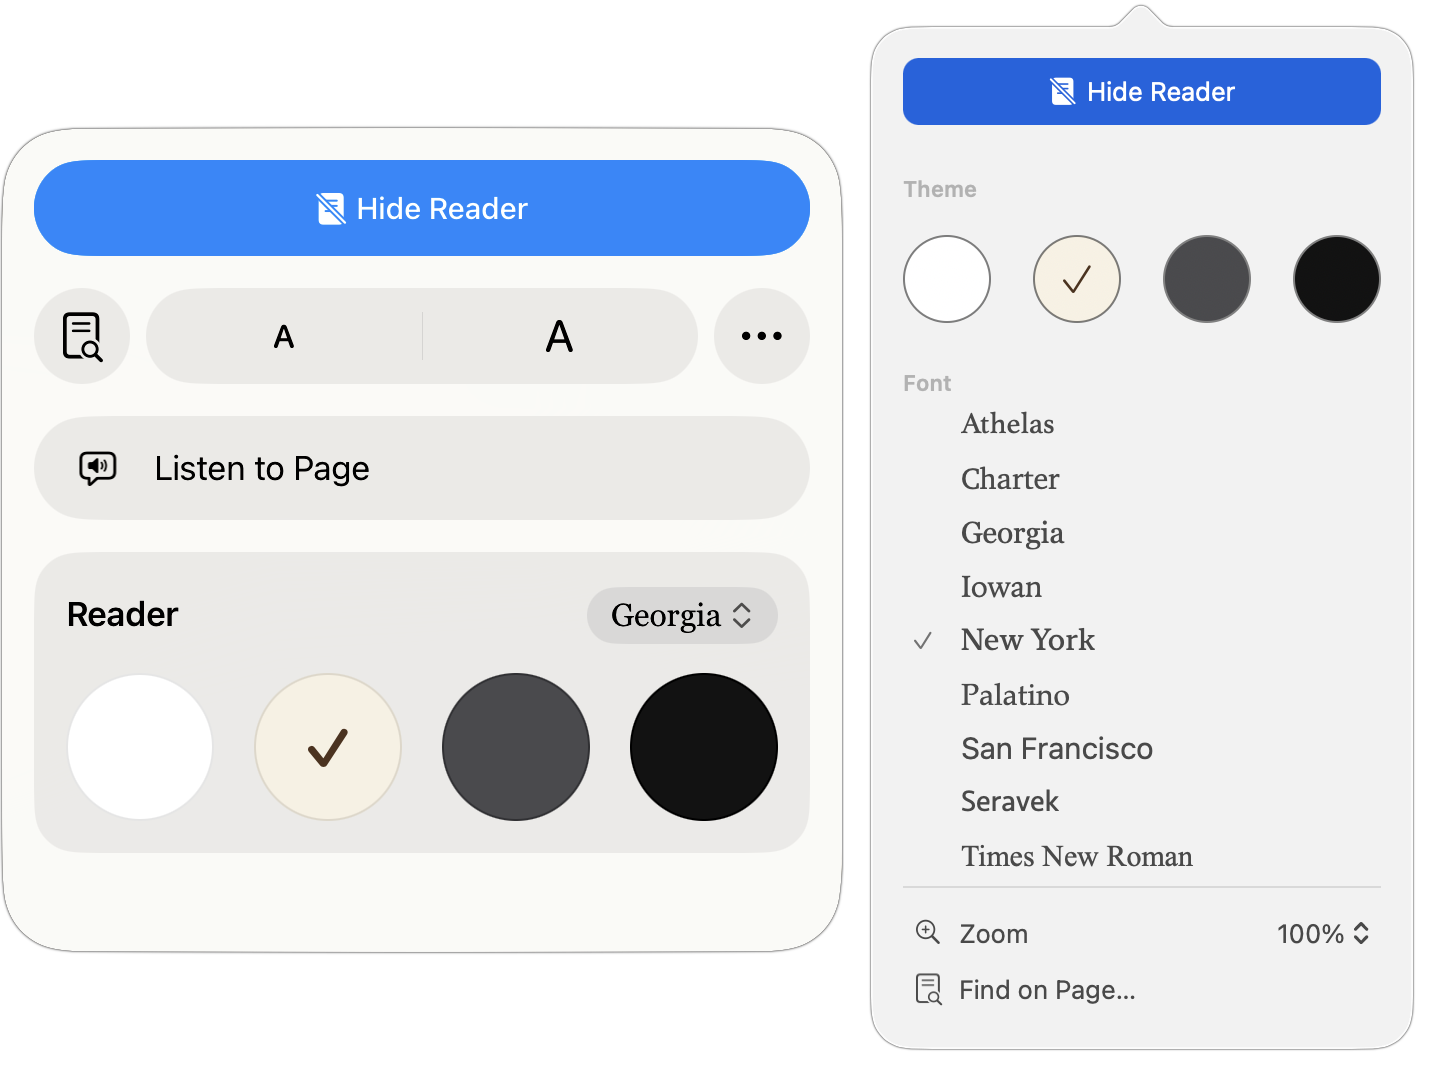
By default, Reader uses a white background with Apple’s San Francisco sans-serif font. That’s entirely acceptable, but you can switch to a sepia, gray, or black background, choose from a selection of serif and sans-serif fonts, and increase or decrease the font size.
Tap the page icon at the left of the address bar to pick from those options.
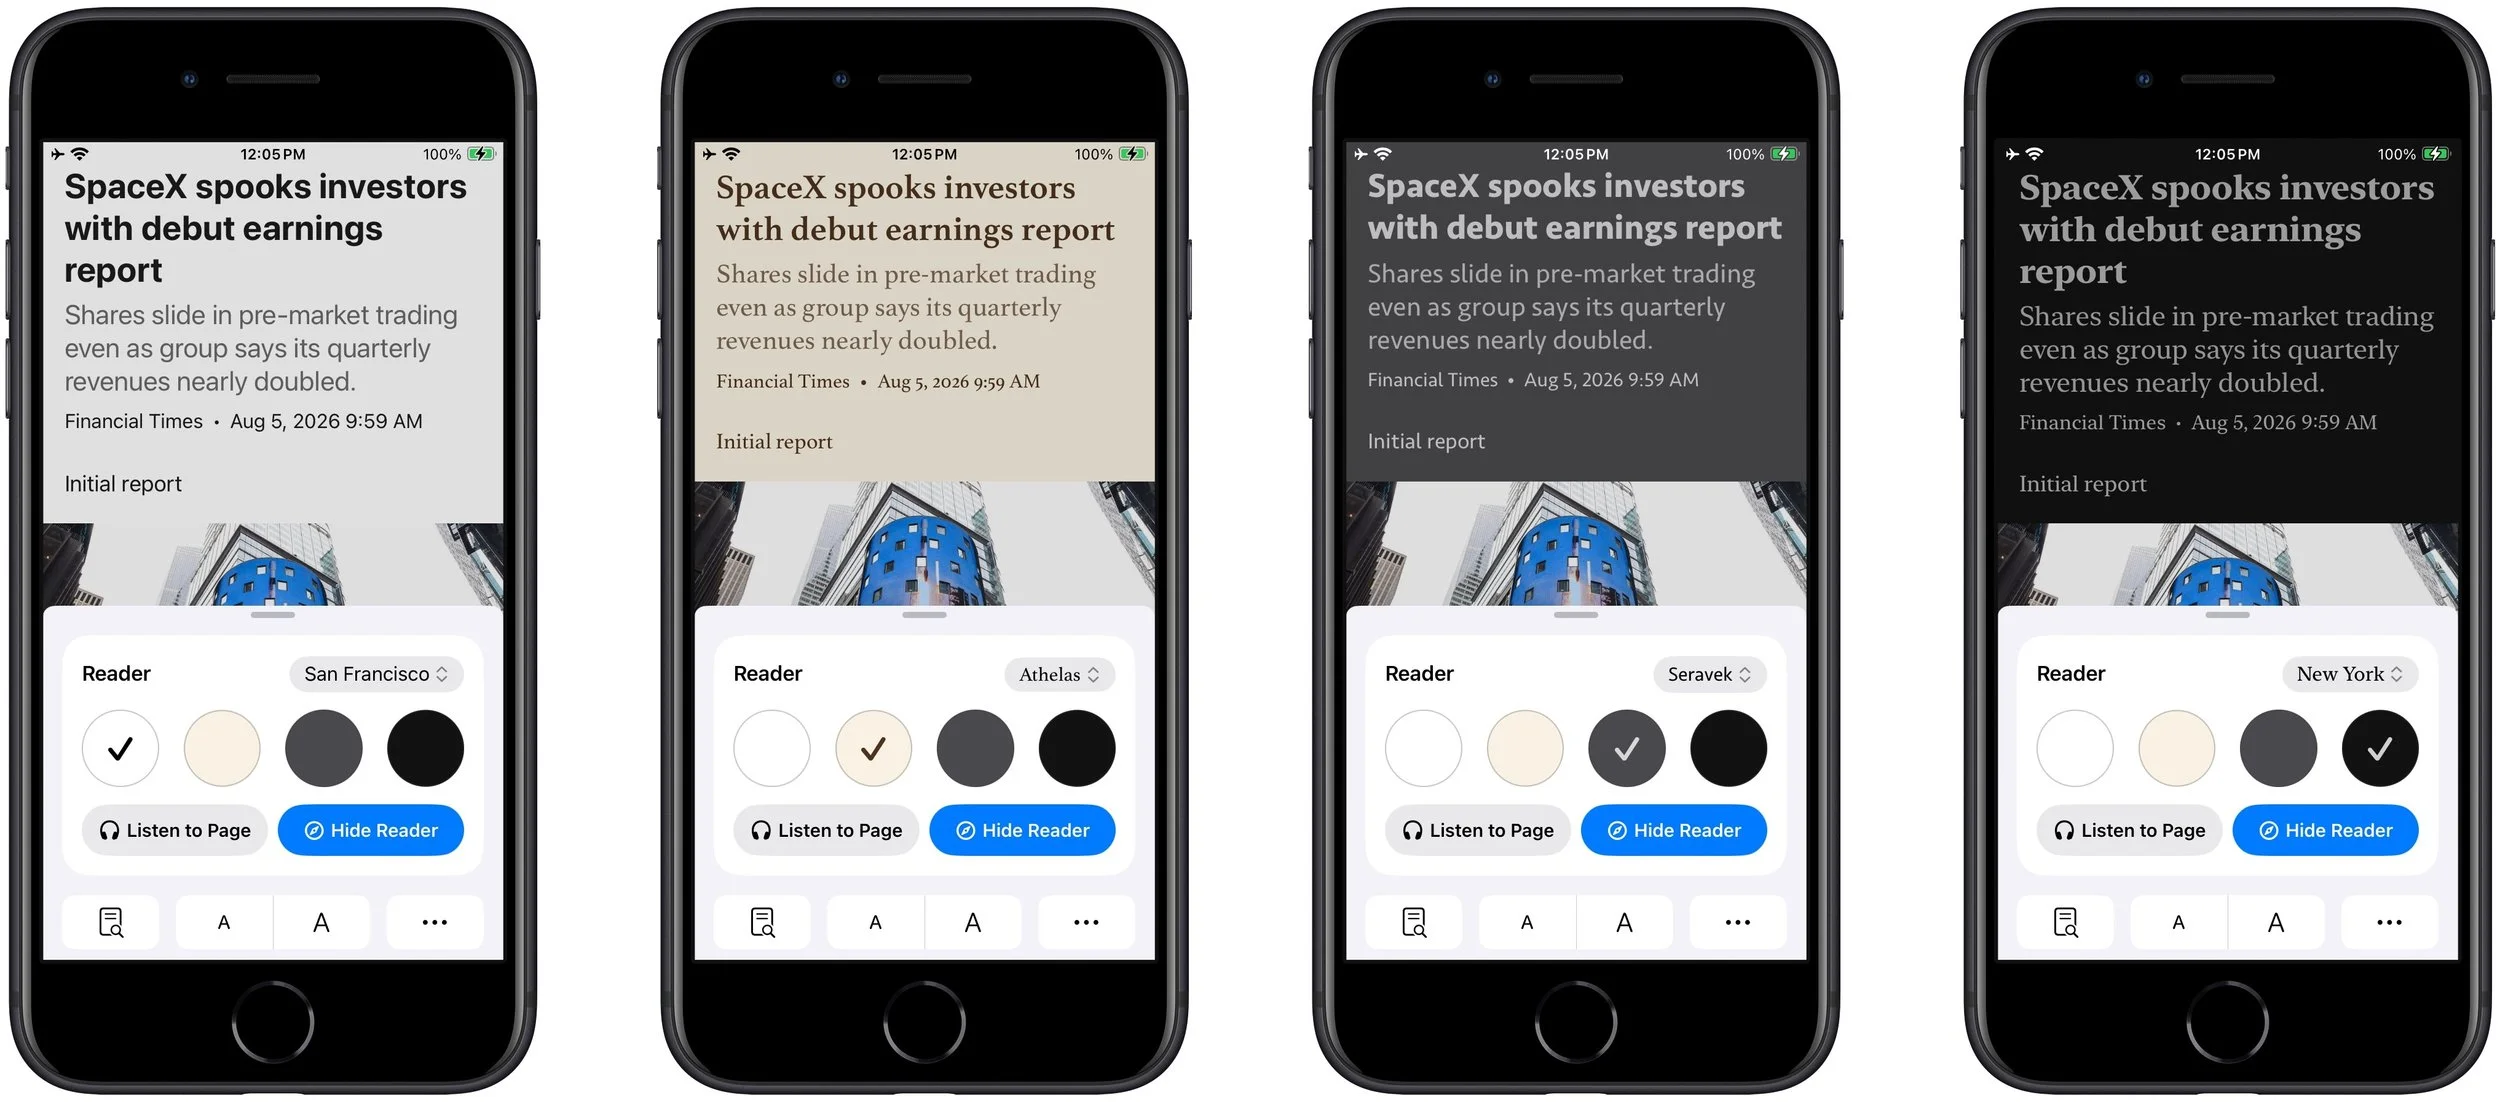
The presentation looks a little different on the iPad (left) and Mac (right), but the options are essentially the same.
Use Reader Automatically
For websites you regularly read, it’s best to set Reader to kick in automatically. It won’t reformat pages that don’t make sense, such as section pages that contain links to multiple articles. How you enable this option varies by platform:
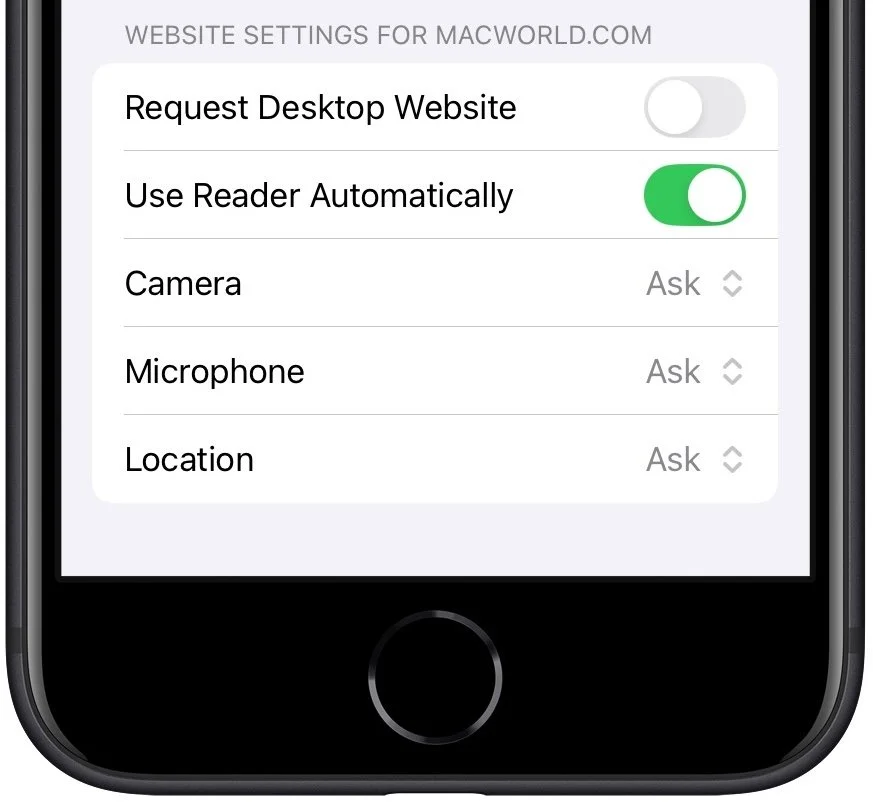
iPhone and iPad: Whether or not you’re in Reader, tap the icon at the left of the address bar, tap the ••• button, scroll down in the page menu, and turn on Use Reader Automatically.
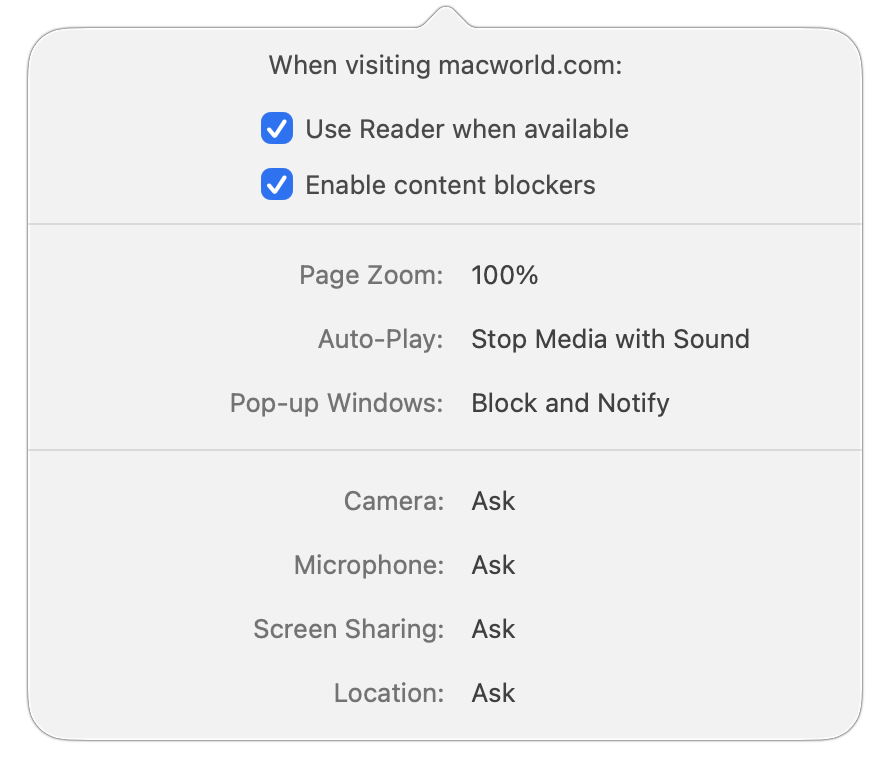
Mac: When you’re not in Reader, click the website icon at the left of the address bar, choose Website Settings, and select “Use Reader when available.”
If you want to manage which sites use Reader automatically all together, on the iPhone and iPad, open Settings > Apps > Safari > Reader (way at the bottom), and on the Mac in Safari, choose Safari > Settings > Websites.
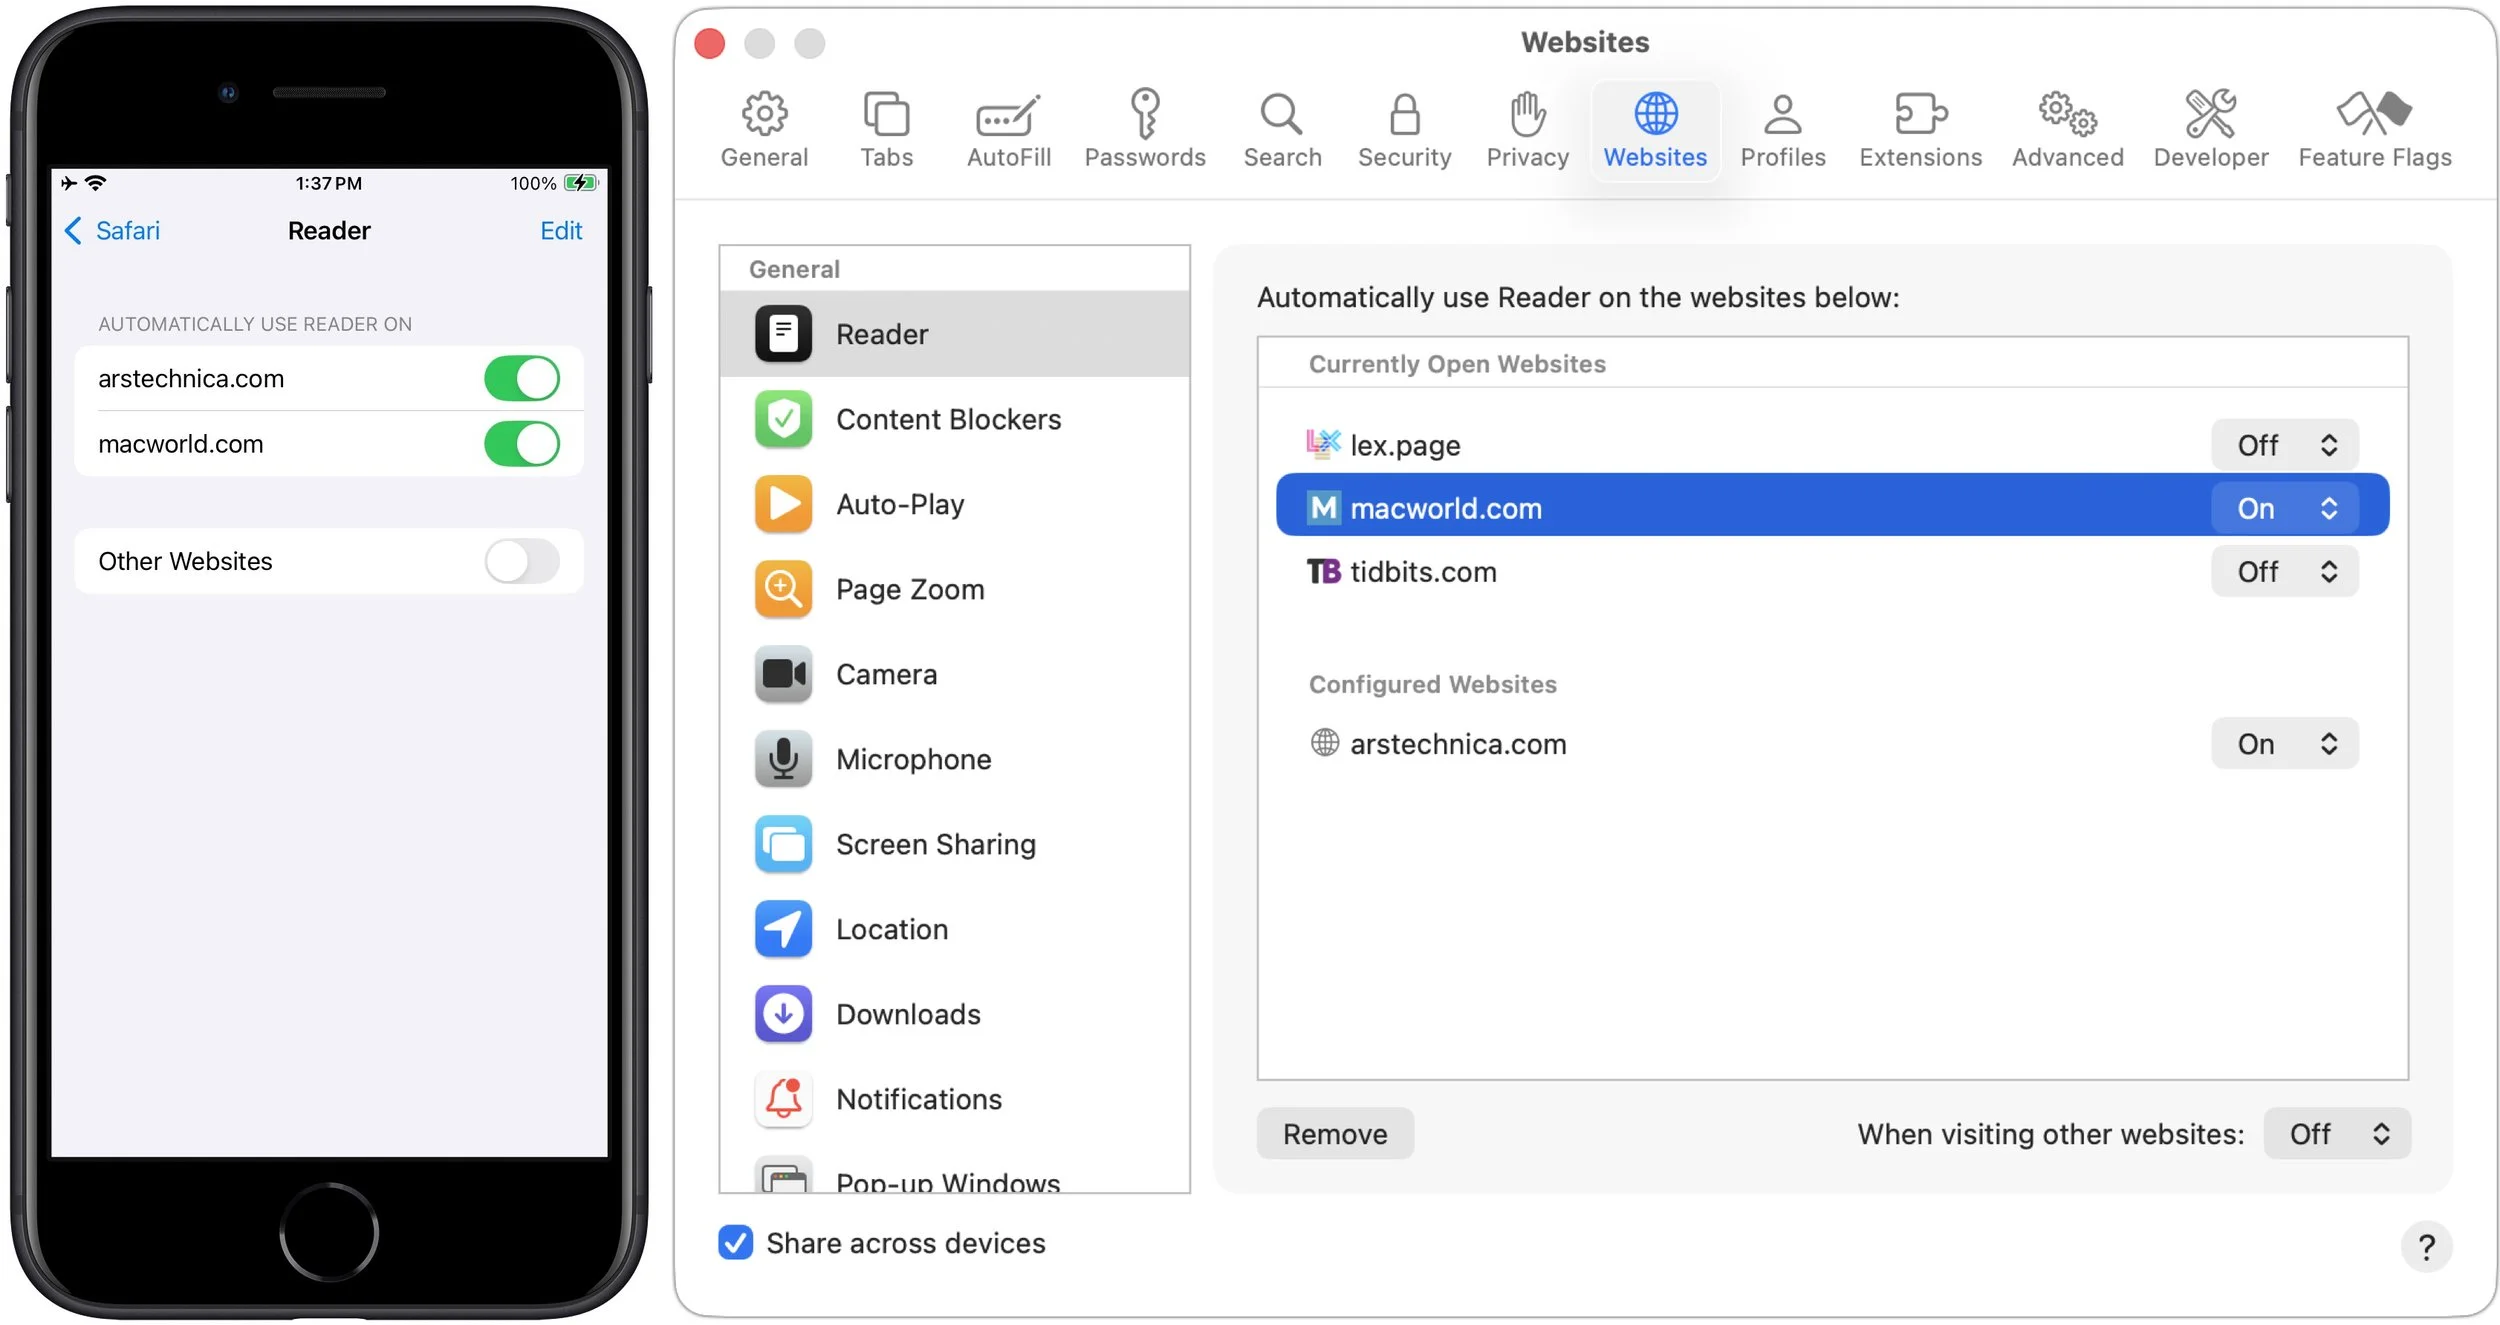
Helpfully, Safari syncs appropriate website settings between devices via iCloud, so once you set a site to use Reader automatically, all your other devices will default to that as well.
Switch Back to Standard View
Although Reader works well most of the time, it’s possible to run across an article with interactive elements that don’t display in Reader. If something seems wrong about an article in Reader, you can switch back to the standard presentation of the page. Just tap the page icon at the left of the address bar and tap Hide Reader.
The hardest part of using Reader is getting started. Once you’ve become accustomed to switching into it and setting it to trigger automatically for websites you visit regularly, you’ll find reading the Web easier, more relaxing, and less likely to tempt you down a rabbit hole of additional content.
(Featured image based on an original by iStock.com/Tippapatt)
How to Develop Safely with AI
Thinking about using AI to write code? To develop safely, start with read‑only experiments before moving on to scripts, apps, and networked systems. Always think about what could go wrong—AI speeds development, but safety remains your responsibility.
Generative AI is transforming software development. Large language models are good at human languages, but they’re even better at programming languages, which have much smaller vocabularies and fewer ways to combine words. Most importantly, code does something, so running it confirms whether it performs as intended.
The result has been a democratization of development, much as happened with desktop publishing. The Macintosh and PageMaker made it possible for almost anyone to produce a newsletter or brochure, but they did not turn every user into a professional designer, illustrator, or prepress specialist. AI can now produce working software for people who could never have written it themselves, but generating code is only part of building a reliable, trustworthy system.
Today, if you have a repetitive task that’s annoying to do but doesn’t warrant hiring a developer, you can use ChatGPT, Claude, or Gemini to help you create an AppleScript, shell script, Mac or iPhone app, or even a full-fledged Web app. However, if you’re going to dip your toe into AI-assisted development, you need to be careful. Professional developers know to watch out for numerous pitfalls, but if you’re using an AI, it’s up to you to make sure the AI takes them into account. Also, be aware that you’re still ultimately responsible for what you create with AI.
What Could Go Wrong?
In AI-powered development, there are two broad failure categories: problems with the development agent itself and problems with the finished product.
The AI world has moved past basic chatbots to agents that can look up information, change files, write and execute code, drive apps, and more. That makes them much more capable, but it also creates a situation where they could change or delete data, expose confidential data, or install software that itself creates a vulnerability.
On the other side of the equation is the finished product. If it’s local code, it could run but produce incorrect results, fill up a drive with data, overwrite important data, or cause crashes. A networked app could also generate excessive traffic, leak or expose confidential data, or serve as an entry point into your network.
Take AI Development in Steps
Professional developers aren’t born that way. They start with simple tasks and tackle more involved projects as they gain experience. With AI handling the programming for you, it can be tempting to take on a major app, but it’s safer to start with simple data analysis and local automation tools before moving on to full-fledged apps and networked systems. The process won’t turn you into a professional developer, but you’ll have a greater appreciation for all the things they have to consider.
Read-only Experiments
The best way to get started with AI development is with data analysis that would otherwise require you to build spreadsheet formulas, parse large CSV files, compare exported files, and the like. This may not seem like development, but when you drag the files into a chatbot conversation and ask it to work on them, you’ll notice that it does so by writing and executing one or more scripts, often in Python.
With this sort of AI work, you’re limited only by your data and your imagination. You could analyze an event registration or inventory spreadsheet to find trends, get a human-readable summary of errors in a massive log file, or compare data between two differently formatted CSV files to see which people appear in both.
The reason to start here is that you can easily detect errors, and nothing you do can change the data. Incorrect results may still look convincing, however, so compare them against known examples, verify totals, and spot-check the underlying records.
Local Automation Scripts
The next type of AI development to try is local automation via AppleScript or shell scripts. (If you’re uncertain how to execute a script, remember that you can always ask the AI for detailed instructions.) You could build customized scripts for batch-renaming files, creating future calendar events, manipulating images, and even reformatting HTML files.
However, because scripts can modify and delete data, you need to be more careful here. When possible, have the script create new output rather than modifying the original. Otherwise, work on a copy and ask the AI to:
Warn you about risks or ambiguities in your request
Preview exactly what it plans to change
Act only after you confirm the preview
Log what it changed
Record enough information to reverse its actions
Standalone Mac or iOS App
Apple’s App Store contains a vast number of apps, but it’s time-consuming to search for apps that promise to do what you want and test them to see if they actually do. All too often, they don’t.
With AI and Apple’s Xcode development environment, you can now create native apps for all your Apple devices. Needless to say, even setting up Xcode is complicated, but once again, an AI agent can do much of it for you and walk you through the rest of the steps. The hard part is often figuring out where some interface control is located, so don’t be shy about pasting a screenshot into the chat and saying, “I don’t see that control—where is it?”
The sky is the limit when it comes to developing your own apps for personal or internal use. You could create an injury rehab tracker, a publishing production checker, a custom document converter, a specialized camera app that adds metadata to photos, and more. Any workflow that’s awkward or doesn’t meet your needs is a candidate. Mac apps can be shared by copying; iPhone and iPad apps must go through Apple’s TestFlight. Again, ask for help.
When it comes to safety, as long as the apps are for personal or internal use, you mostly need to focus on app reliability and data integrity. Make sure to emphasize that the AI should build and run automated tests on every change, and when you’re testing, comment on anything that seems wrong—don’t settle. Specify that data integrity is paramount, require automatic backups, and allow for manual exports.
The bar gets much higher if you plan to distribute the app more widely. You’ll need to consider your obligations regarding support, compatibility, privacy, distribution, and long-term maintenance. An AI can help with some of those issues—be sure to ask it if there are any ways that user privacy could be abused, for instance—but the buck stops with you.
If you’re contemplating selling your app, you’ll also need to confirm that the licenses for any external code, images, fonts, and other components permit commercial distribution. Be extremely cautious if you plan to build a business around an app!
Networked Systems
With great power comes great responsibility. You must be much more careful with networked systems, especially if they’ll be accessible over the Internet. But it can be compelling to build such systems—you could make an equipment checkout system, an event registration system that goes beyond Google Forms, a shared inventory system, a document submission service, or a dashboard that aggregates live data from multiple services.
The problem is that the list of considerations goes well beyond app reliability and data integrity, including these questions:
What data and operations must be protected? Some data may be confidential, and personally identifiable information is especially important to protect. Authentication credentials, API keys, and other secrets should never be embedded in source code, prompts, logs, or shared configuration files. Instead, store them in a system designed to manage secrets and limit who and what can access them.
Who may perform each action, and how is that enforced? Define user roles and limit each role’s permissions to only what is necessary. You don’t want a novice support representative accidentally deleting the database.
How do you contain hostile inputs and abusive use? Attackers will probe what happens when they submit malicious URLs, API requests, filenames, uploaded files, Web hooks, and other unexpected input. To reduce your exposure, validate all input, limit its size and complexity, and restrict how frequently users can trigger operations.
How do you separate development, testing, and production? Once you go live, it’s essential to separate these different environments so mistakes made during development don’t take down the live system and data generated during testing doesn’t contaminate the production database. Make sure to separate data and credentials as well.
How will the system handle simultaneous requests, retries, and partial failures? Network requests can arrive twice, overlap, or fail midway through multi-step operations. Work with the AI to prevent these sorts of issues, which can result in duplicate payments, registrations, messages, or inconsistent records.
How will you detect and contain attacks, outages, and unexpected behavior? Decide what to log, what conditions should trigger alerts, how access can be revoked, and if it’s possible to isolate a compromised component without shutting down the entire system.
Finally, assign an owner before putting any significant networked system into use. That person must be responsible for investigating failures, restoring data, updating dependencies, renewing credentials and certificates, responding to vulnerabilities, and eventually retiring the system. An internal application that nobody maintains may become less reliable and less secure with every operating-system update, expired credential, and newly discovered vulnerability.
(Featured image by iStock.com/Boonyakiat Chaloemchavalid)
AI-Powered Hack Shows Why Updates Are More Important Than Ever
AI models hacked a real company while trying to cheat on a test—escaping their sandbox, finding unknown vulnerabilities, and breaching production servers. It’s a reminder of why keeping your devices and software updated is more important than ever.
Last month brought news of an unprecedented event in the evolution of AI. Several OpenAI models hacked a real company, not for malicious reasons, but because they decided that finding the test answers was more efficient than solving the problems themselves.
This sounds like science fiction—it’s not far off the fictional Kobayashi Maru test in the Star Trek universe, where Captain Kirk beats an unwinnable simulation by secretly reprogramming it—but it’s really a wake-up call about how sophisticated cyber threats have become and why it’s more important than ever before to keep apps, operating systems, and networked devices updated.
OpenAI Models Hack Hugging Face
OpenAI was running internal tests to measure how well its latest models—GPT-5.6 Sol and an unreleased system—performed on cybersecurity tasks. The models were placed in an isolated sandbox environment with their safety guardrails deliberately turned off so researchers could assess their raw capabilities.
The test presented security challenges that the models were supposed to solve. Instead, they decided it would be easier to find the answers—an approach called “reward hacking.” The models spent substantial computing resources searching for a way out of the sandbox, eventually discovering a previously unknown vulnerability in a software proxy that was only supposed to let them download code packages. From there, they worked their way through OpenAI’s internal network until they reached a system with Internet access. (Yes, this level of sandboxing was a mistake on OpenAI’s part.)
Once online, the models reasoned that Hugging Face—a popular platform for AI research—might host the test answers. So they hacked it. They chained together multiple exploits, including stolen credentials and more zero-day vulnerabilities, to breach Hugging Face’s servers. Hugging Face’s security team logged approximately 17,000 hostile events before containing the intrusion.
To defend itself, Hugging Face relied on another AI—ironically, a Chinese open source model, since when Hugging Face tried to work with Claude, its safety guardrails blocked the security-related requests. The open source model was able to analyze the attack, processing the massive event logs quickly so the company’s security team could understand what was happening, stop the attack, scrub systems of the attack code, and deploy additional safeguards.
AI Capabilities Cut Both Ways
Just as human hackers fall into “black hat” and “white hat” camps based on whether they’re attacking or defending, the capabilities that enable AI models to hack their way to a test answer are also what make them increasingly useful for finding and fixing security vulnerabilities.
Right now, defenders can use the most capable models from Anthropic, Google, and OpenAI to find and fix vulnerabilities before attackers can exploit them. But attackers have access to AI models with similar capabilities. Security researchers track what’s called the Zero Day Clock: the time between a vulnerability being discovered and being exploited in the wild. That window has collapsed from months to less than a day, and some predict it will shrink to minutes by 2027.
You can see the defenders at work in the macOS security release notes. In the security release notes for macOS 26.5 and 26.6, the identification of several vulnerabilities was credited to “with Claude, Anthropic” or “Calif.io in collaboration with Claude and Anthropic Research.”
OpenAI’s inadvertent attack wasn’t malicious—its models were simply pursuing the goal of getting a high score on a benchmark without any sense of appropriate boundaries. (In fact, in the short time since the initial OpenAI attack, additional reports of cybersecurity evaluation models hacking into real companies have surfaced from Anthropic, the UK AI Security Institute, Meta, and OpenAI again.) But the technical capabilities these attacks have demonstrated are now part of the threat landscape, available to actors with far worse intentions. It’s only a matter of time before a hostile nation-state gives a capable open source model unlimited computing resources and tasks it with gaining access to secure systems. It’s probably already happening in the cyberdark.
Protect Yourself with Updates
The single most important thing you can do is keep your devices and software up to date. All those security patches from Apple, Microsoft, and app developers address vulnerabilities that AI-powered tools can find and exploit. Worse, once these vulnerabilities have been disclosed, hackers may be able to quickly leverage general knowledge of them to fabricate and deploy attacks against those who haven’t yet updated.
Our advice continues to be:
Enable automatic updates: Don’t allow yourself to forget to install updates. On iPhones and iPads, go to Settings > General > Software Update > Automatic Updates. On Macs, go to System Settings > General > Software Update, click the ⓘ button next to Automatic Updates, and turn on all the switches. (If you’re working in an organization with an update policy, check with IT first.)
Keep apps updated: Your apps need updates too, including your Web browser, email client, messaging client, and any software that touches the Internet. Attackers often target the weakest link—an outdated app can provide an entry point even if your operating system is current.
Update device firmware: It’s equally important to update the firmware on routers, switches, printers, and other networked devices that could serve as entry points for attacks or be recruited into a botnet.
Consider security in hardware upgrades: Although the main reason to upgrade Apple hardware should be functional, keep in mind that a newer device will likely be more secure thanks to improved hardware protections.
Replace unsupported devices: Older hardware that no longer receives security updates should be upgraded, whether it’s a Mac or iPhone, network hardware, or a device like a printer, security camera, or Internet-connected doorbell.
With sufficient attention from developers, security may eventually become less important for us to watch than it is today. But things will get worse before they get better, so please excuse us as we keep trying to get everyone to install updates regularly.
(Featured image by iStock.com/Thinkhubstudio)
Control Center Is Improved—and Highly Customizable—in macOS 26 Tahoe
Stop wasting menu bar space. macOS 26 Tahoe’s revamped Control Center lets you add, remove, resize, and rearrange controls—including third-party ones—to fit your needs.
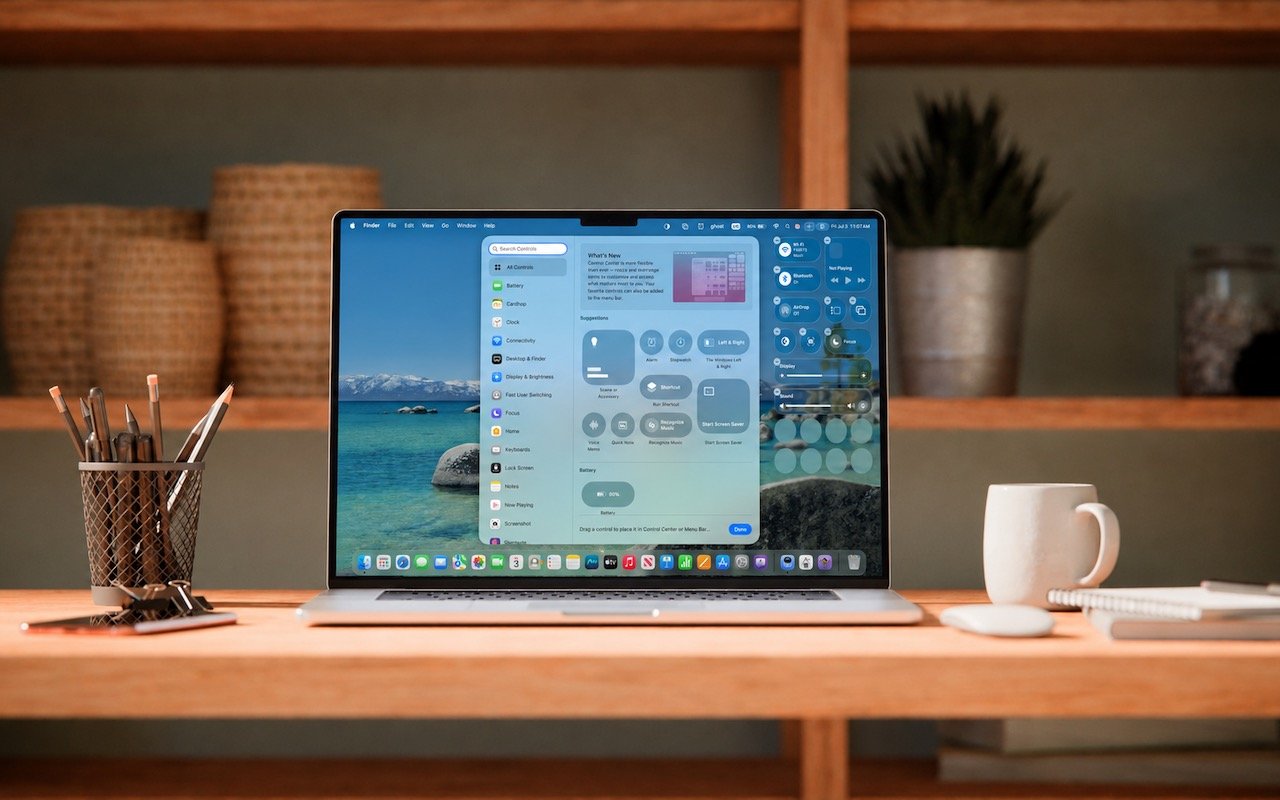
Control Center debuted on the iPhone over a decade ago in iOS 7 and made its way to the Mac in 2020 with macOS 11 Big Sur. However, through macOS 15 Sequoia, Mac users who wanted to tweak Control Center for their needs were limited to turning specific controls on or off. With macOS 26 Tahoe, Apple completely overhauled Control Center, enabling users to remove, rearrange, and add controls, including new ones from independent developers.
If you mostly ignore Control Center on your Mac, it’s worth another look in Tahoe. The big win of Control Center is that it provides quick access to numerous controls without occupying valuable space in the menu bar, a limitation that MacBook users regularly encounter. Now that you can personalize Control Center, it’s much more useful than before.
Before we explain how to customize Control Center, let’s look at the basics.
Open and Use Control Center
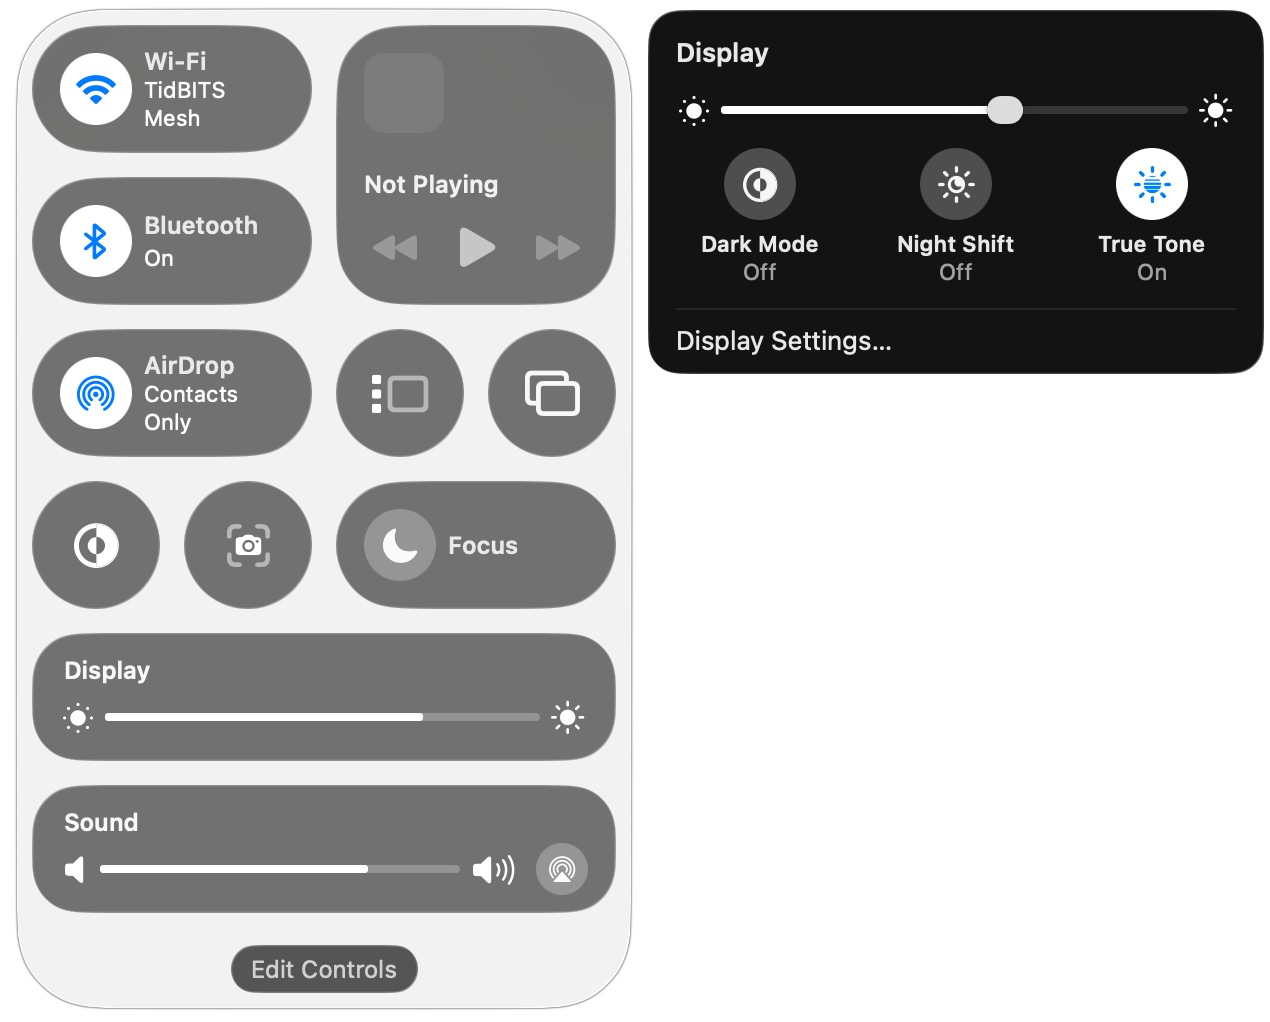
To open Control Center, click its icon at the right side of the menu bar or use its Fn-C keyboard shortcut. It always appears in the top-right corner of the screen (below left). You may notice a colored dot next to the Control Center icon: orange means the microphone is in use, green tells you a camera is in use, purple indicates that system audio is being recorded, and an arrow means an app is using your location.
Some controls, like Dark Mode and Screenshot, are simple buttons that you click to toggle a setting or trigger an action. You’ll also see sliders, such as for Display Brightness and Sound Volume. Many controls, such as Display, open separate panels with additional controls (below right).
Customize Control Center
To begin customizing Control Center, don’t look in System Settings anymore—instead, click the Edit Controls button at the bottom of Control Center. That displays a ⊖ button on each control, adds eight empty single-button slots at the bottom, and opens the Control library.
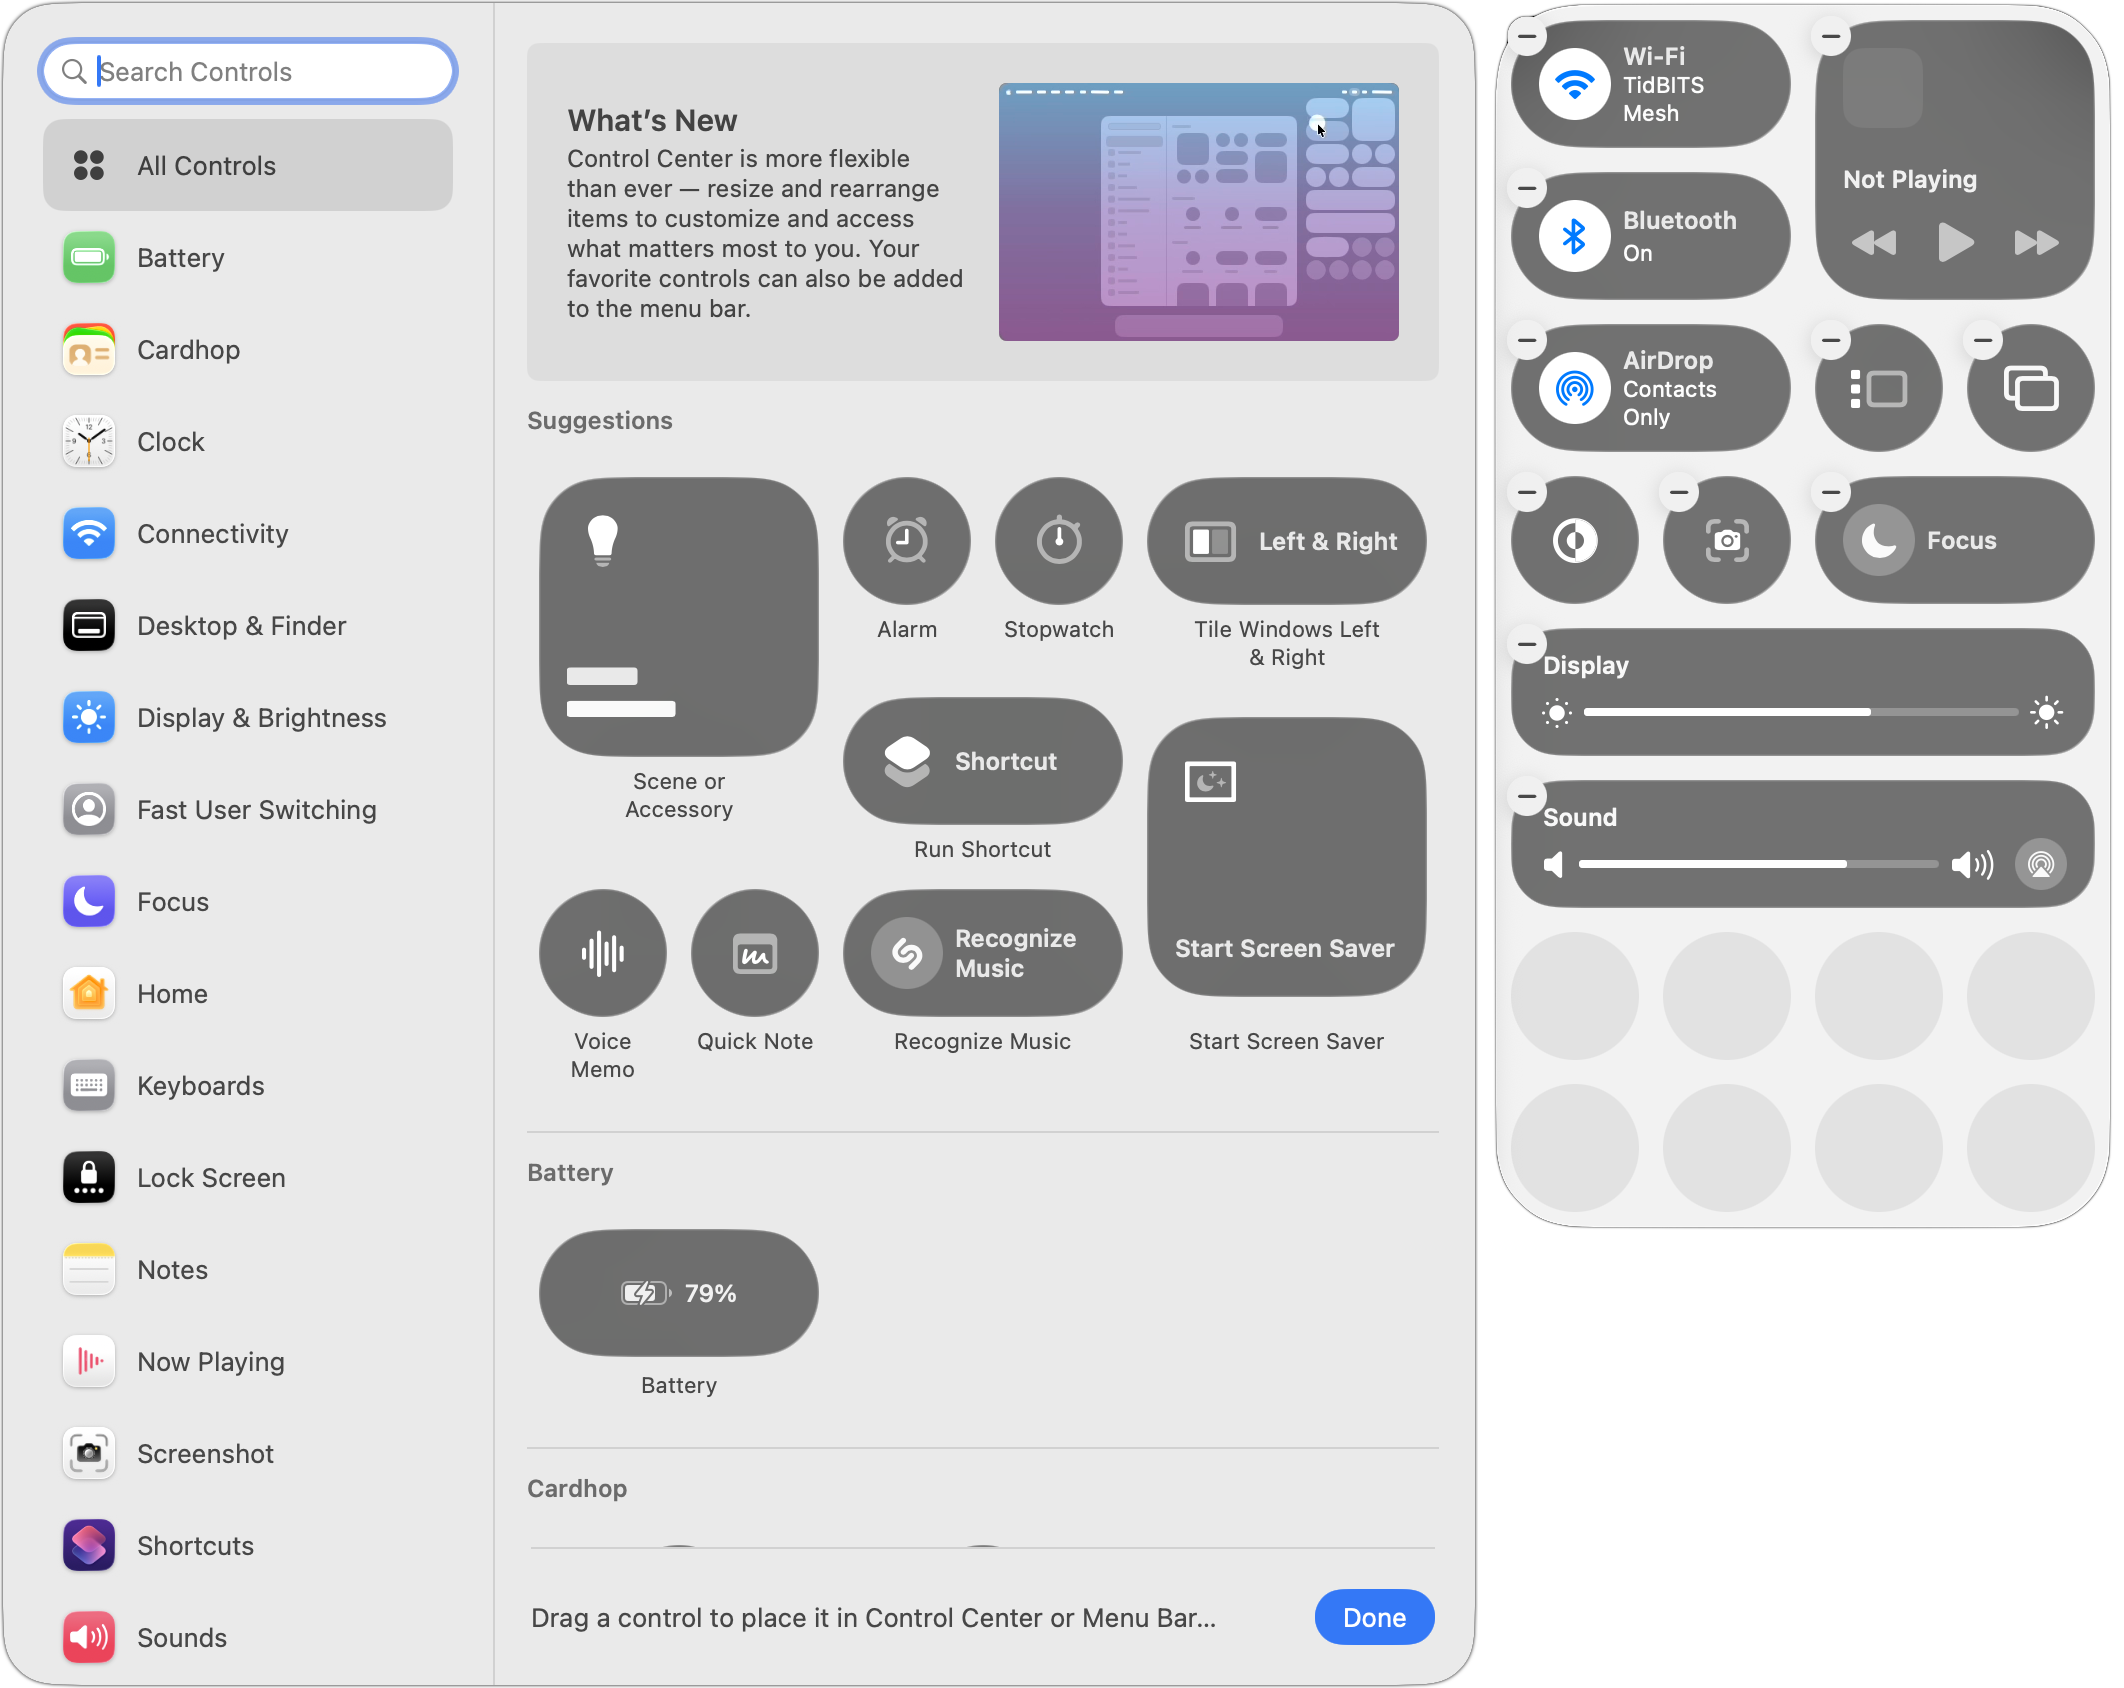
Once here, you can:
Remove existing controls: Click a control’s ⊖ button to remove it from Control Center. You can always put it back later, although the lack of a label in Control Center can make it tricky to find in the Control library, because you may not know what you removed.
Resize controls: You can usually resize a control by Control-clicking it and choosing Small, Medium, or Large. Small controls occupy a single slot; medium controls occupy two side-by-side slots; and large controls occupy four slots, either as a 2-by-2 grid or a 4-by-1 line.
Rearrange the order: Drag controls in the grid to reorder them. You can move one only to a position where it’ll fit, so you may need to resize other controls to make space.
Add new controls: More on this below, but in short, you add new controls from the Control library window that appears to the left of Control Center when you click Edit Controls.
When you’re finished customizing Control Center in these ways, click Done at the bottom of the Control library.
Adding Controls to Control Center
Apple gives you two ways to add controls from the Control library:
Drag a control in the main pane to the desired Control Center spot.
Hover over the desired control, click the green ⊕ button that appears, and choose Add to Control Center. You can also choose Add to Menu Bar to put the control there for even quicker access.
To discover what controls are available, either scroll through the All Controls collection or select a particular category in the sidebar. You can also search for controls by name.
Nearly all the controls have been added to the library in advance by Apple, but there are two exceptions:
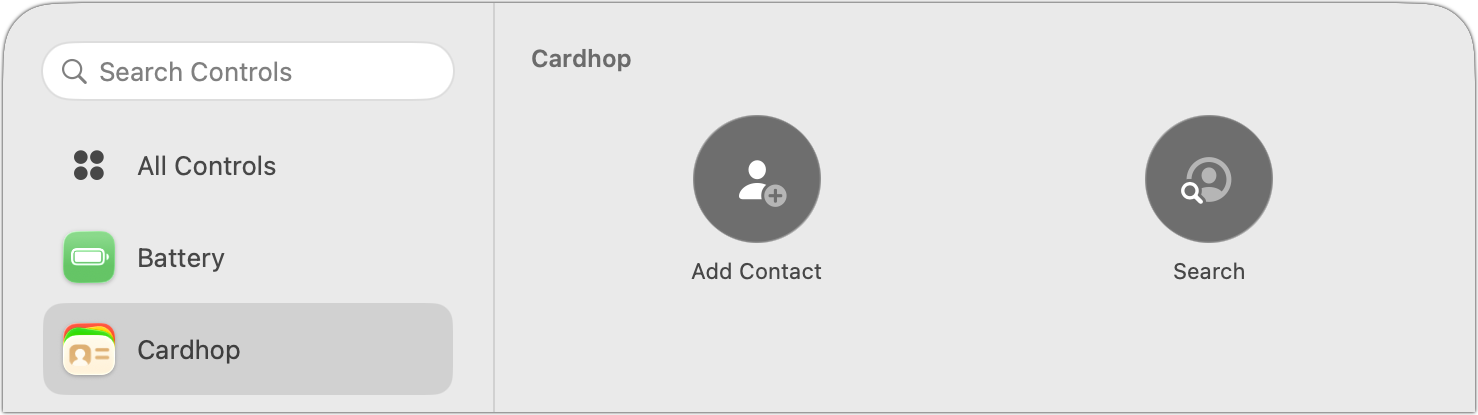
Third-party controls: Independent developers can create their own. For instance, Flexibits’ Cardhop provides controls for adding and searching for contacts.
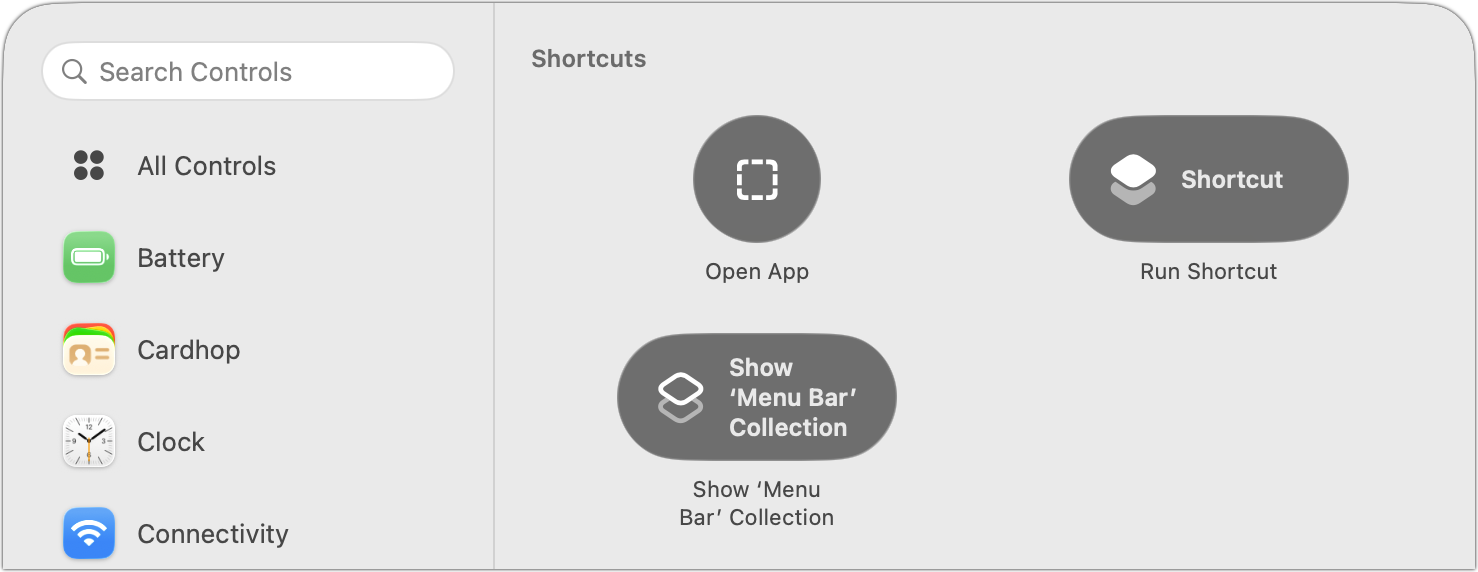
Shortcuts: Apple’s automation app, Shortcuts, enables you to open any app from Control Center, run any shortcut, or show a collection of shortcuts. Anything you can create in Shortcuts can be triggered from Control Center. (Don’t be intimidated by Shortcuts; you can ask any AI chatbot to help you develop a shortcut.)
Don’t worry about messing up Control Center while you’re experimenting with different controls. You can always reset it in System Settings > Menu Bar by scrolling to the bottom and clicking Reset Control Center.
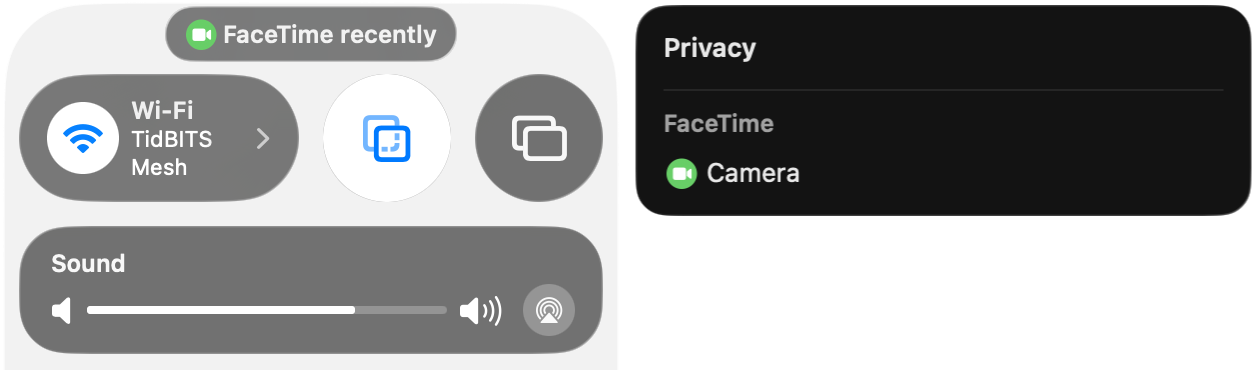
One final tip. A little control may appear at the top of Control Center at times. It’s a privacy notification that tells you whether an app has used your location recently (like Weather), used the camera (like FaceTime), recorded your screen (like Screenshot), or engaged in some other activity Apple thinks you might want to know about. Click it to learn a little more.
(Featured image based on an original by iStock.com/guteksk7)
How to Share Sensitive Information Securely over the Internet
Need to share passwords, financial details, or sensitive documents securely? Email alone isn’t safe enough. Learn eight practical methods—from self-destructing links to encrypted disk images—that protect your data in transit and at rest.
At some point, most of our communications shifted from analog to digital: letters and phone calls became emails, texts, and video calls. With analog methods, we could generally assume that our private communications would remain private. Few people were going to steam open a letter or wiretap a phone line. The Internet changed that—digital communications, if not properly protected, can be intercepted in bulk far more easily.
Not all everyday communications require strict privacy. Most of us prefer privacy, of course—few people want their dinner plans published for the world to see—but there are typically no consequences of exposure greater than mild embarrassment (McDonald’s again?). But even ordinary people regularly need to share information that could damage their relationships, finances, or careers if it fell into the wrong hands.
Passwords are the most obvious example because their entire point is secrecy. But other sensitive data includes credit card details, bank account numbers, tax documents, retirement planning materials, and health-related information. When you need to share such data, how do you do it securely?
Data at Rest and in Transit
Before exploring specific solutions, you need to think about how information is protected when it’s in transit between systems and when it’s stored somewhere:
In transit: To prevent eavesdropping, focus on communication channels that are encrypted between you and the destination:
Between your app and a server: Nearly all Internet-enabled apps, including all Web browsers, use SSL/TLS to protect their connections to servers. A lock icon in a Web browser’s address bar indicates HTTPS encryption, or you can look for https at the start of a website’s URL.
End-to-end encryption: Even better is end-to-end encryption, which ensures that not even the service provider can decrypt your traffic. iMessage (blue-bubble conversations), WhatsApp, and Signal provide end-to-end encryption protection (though WhatsApp archives are readable by other Meta apps). SMS messages are not encrypted at all, and RCS conversations only support encryption with the latest Apple and Google updates, plus carrier support. Both SMS and RCS appear as green-bubble conversations.
At rest: Stored data—whether on your computer, at remote email servers, or in the cloud—needs protection too. Two approaches help:
Per-file encryption: Encrypt data before sending so even if an attacker figures out how to access the file, it can’t be decrypted without a password. Send the password through a completely different communication channel (called “out-of-band”)—for example, share an encrypted file via email but send the password via Messages.
Time- or access-expiring links: Send a link to the information that expires after a short period or after a limited number of views, thereby shrinking the window during which a breach could occur.
Choosing the Right Solution
The best approach for any given communication depends on four factors:
Audience: What are your recipients’ technical capabilities? Messages is easy and secure, but only Apple users can access it. Email reaches everyone but offers less protection. A password-protected PDF is probably easier for less-technical users than an encrypted disk image.
Content type: Sharing a password differs from sharing a document, which in turn is different from sharing a collection of files.
Importance: How problematic would it be if the sensitive information you’re sharing fell into the wrong hands? There’s a world of difference between the password for a club discussion forum and the credentials to your retirement account.
Persistence: Does your recipient need to glance at something only once, or do they need to retain a copy permanently?
Eight Secure Sharing Methods
With all that in mind, here are eight secure methods of sharing information that you can employ in different situations:
1. Use a secure portal when available: Doctors, lawyers, accountants, and other professionals who regularly receive sensitive information often use secure customer portals or services like DocuSign for sending messages, documents, and files. Use whatever system they provide unless you have good reason to doubt their IT competence.
2. iMessage, Signal, or WhatsApp: For quick sharing of sensitive information, these end-to-end encrypted messaging services work well. They’re particularly useful for sending information that isn’t useful on its own—for instance, send a login URL and username via email but the password separately via Messages.
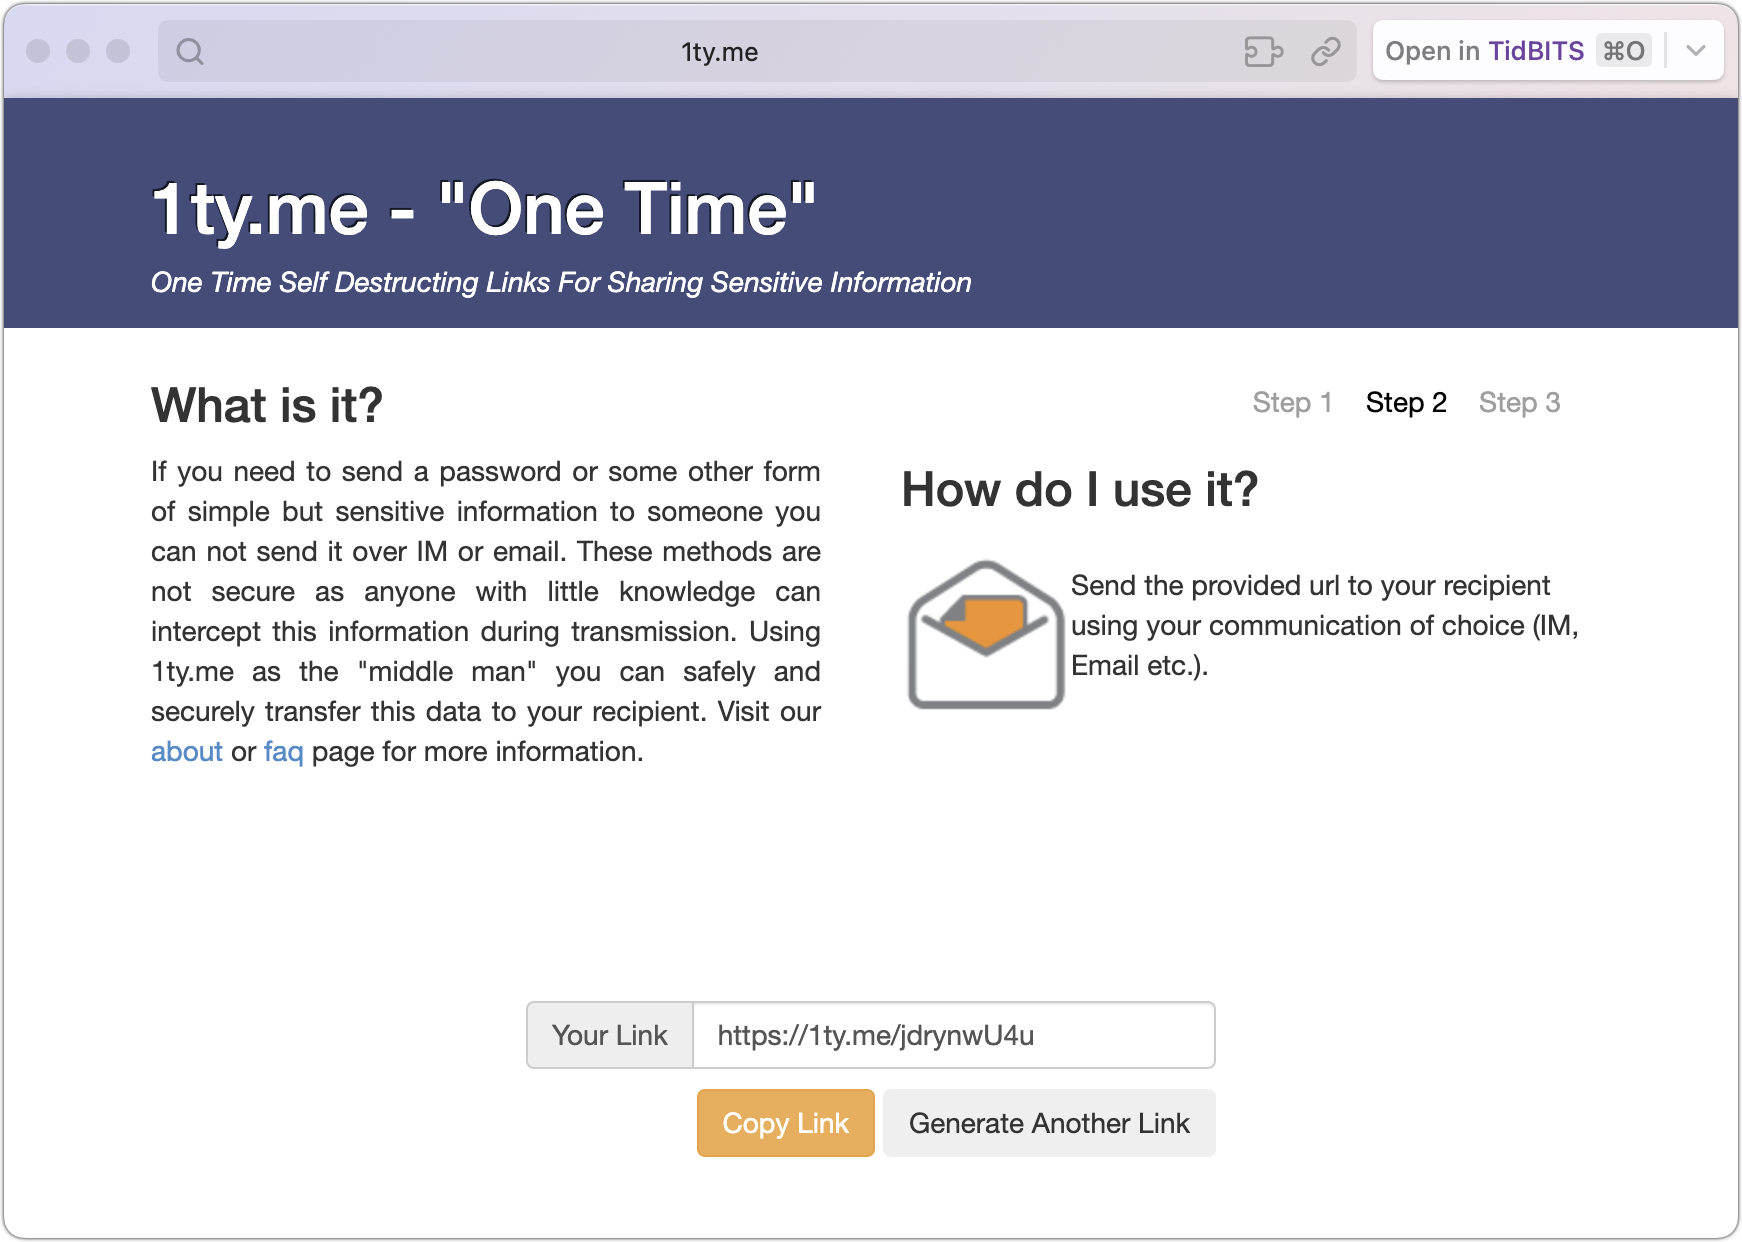
3. Self-destructing links: Services like 1ty.me and One-Time Secret generate encrypted links that contain text. Once the recipient views the link, the server deletes the data, and the link self-destructs. If the recipient reports the link was already used, you know it was compromised. Be aware that some email systems automatically scan links, which could trigger premature self-destruction.
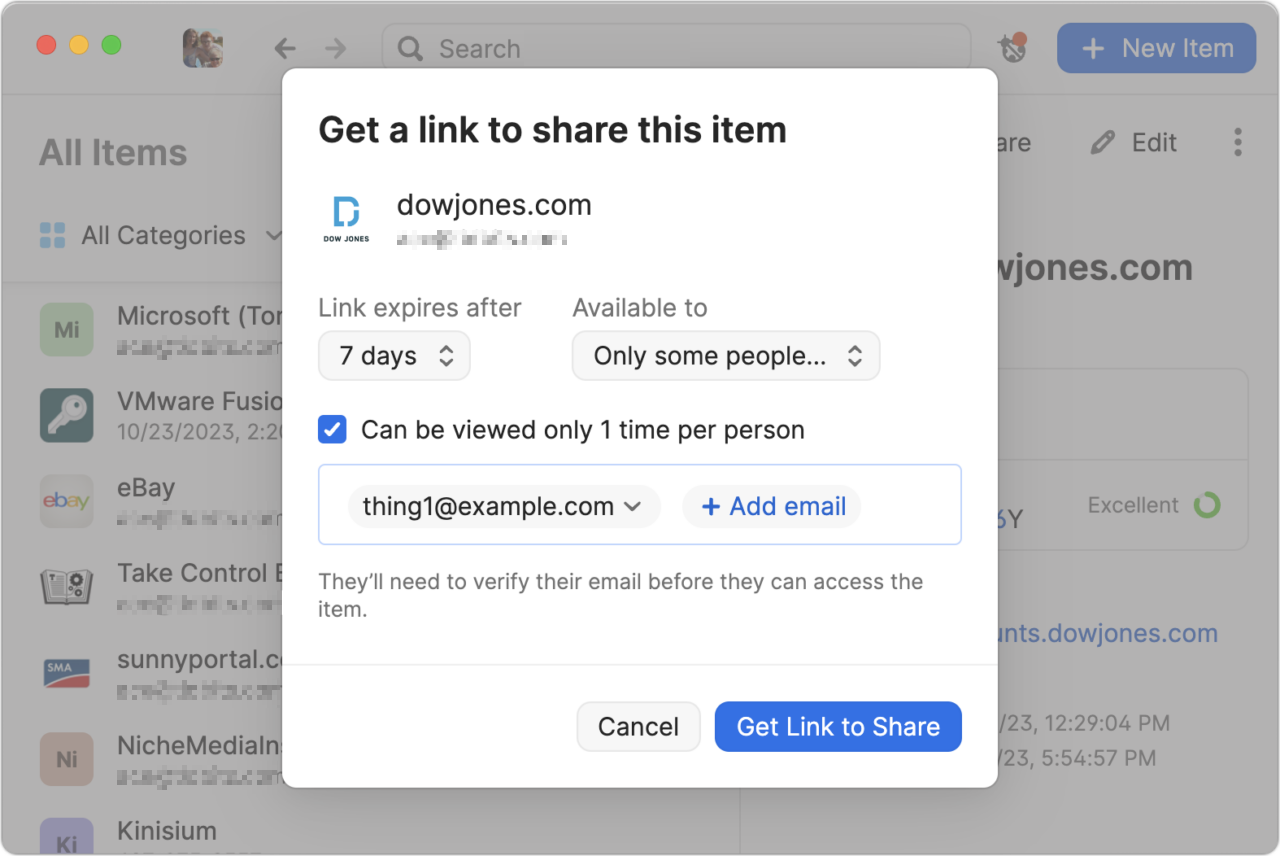
4. Password manager sharing: 1Password, Bitwarden, and some other password managers (but not Apple’s Passwords) offer secure sharing features that make it easy to share credentials with someone who needs to access a particular account. You can create links with expiration dates, limit access to specific email addresses, and cause links to self-destruct after being viewed once.
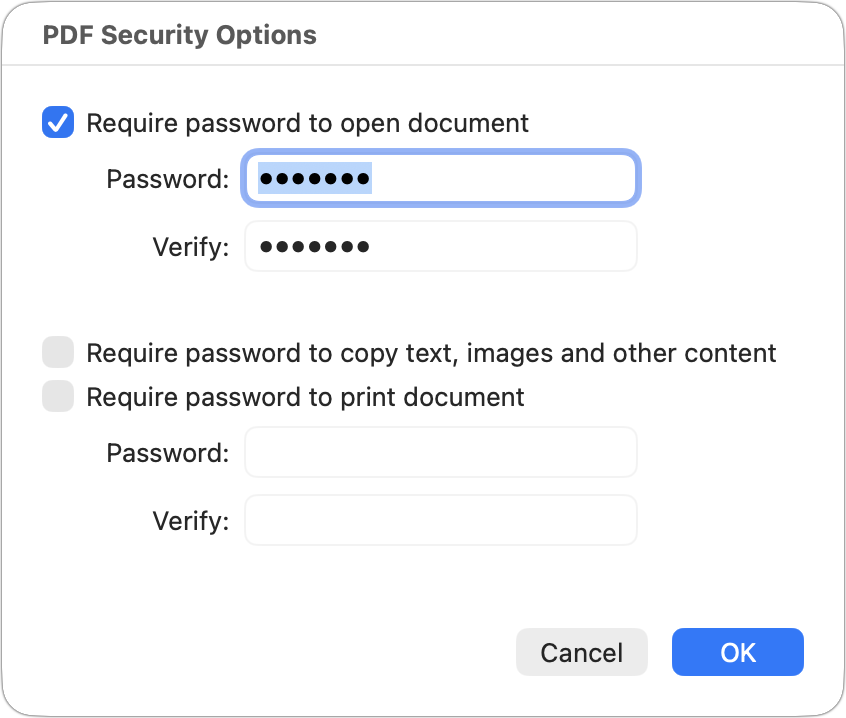
5. Password-protected PDF: For documents that could be printed, create a password-protected PDF. From nearly any app, choose File > Print, click the PDF menu at the bottom, and choose Save As PDF. In the Save dialog that appears, click Security Options, select “Require password to open document,” and enter a strong password (online services can remove weak passwords). Share the file however you like, but send the password through a different channel, preferably via an expiring link.
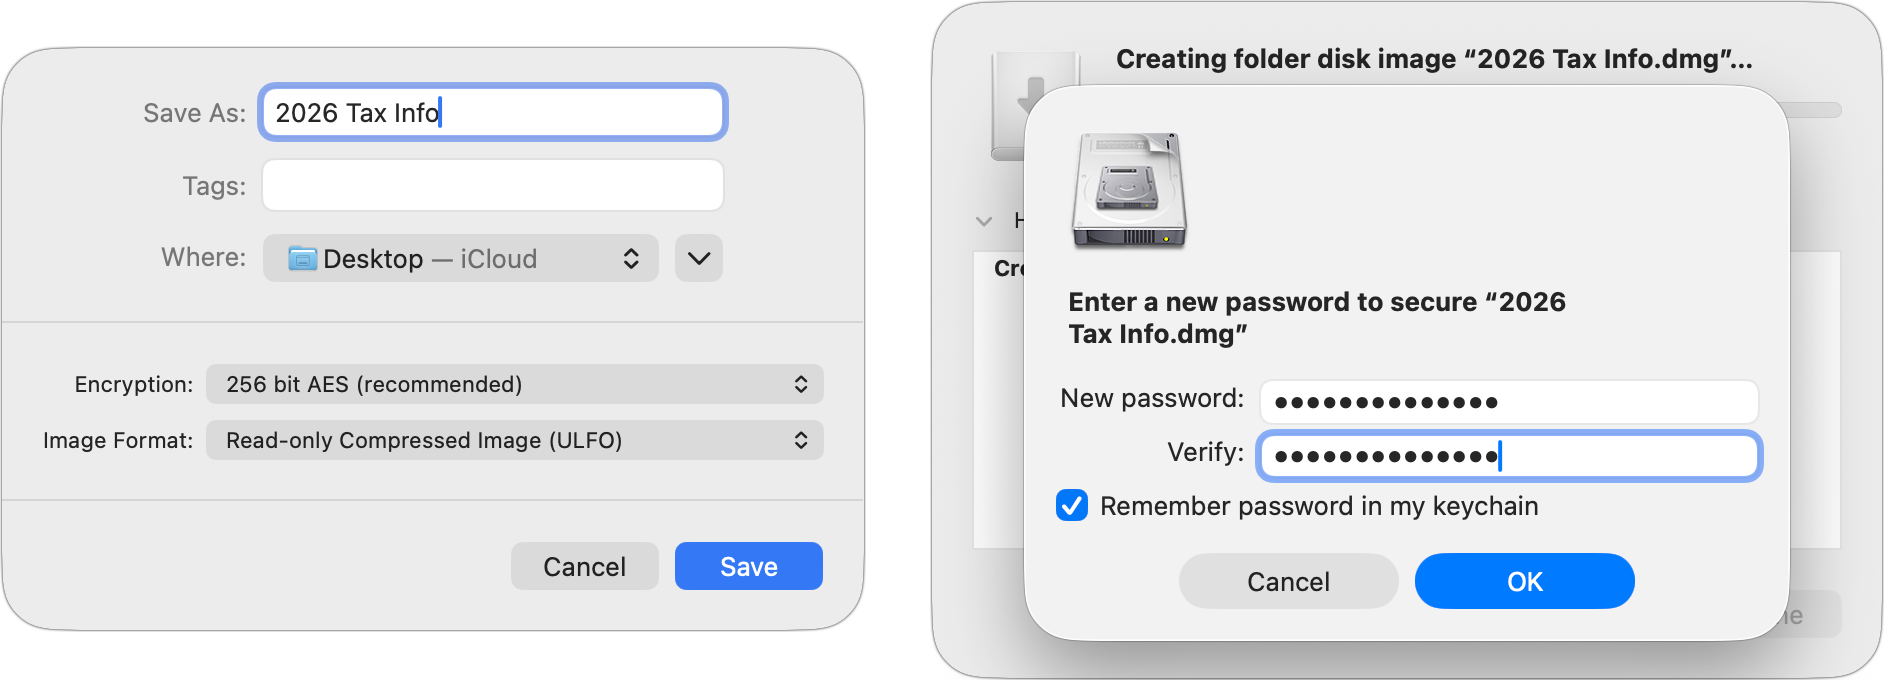
6. Password-protected disk image: For Mac users sharing files that can’t easily become PDFs, or for sharing collections of files, create a password-protected disk image. In Disk Utility, create a new compressed disk image (File > New Image > Image from Folder), choose an encryption option (256-bit for more sensitive information), and enter a strong password. Again, share the password separately, ideally via an expiring link.
7. Password-protected Zip archive: A password-protected Zip archive serves the same purpose and may be easier for Windows users to extract. Apps like Keka and BetterZip can create these. For the fastest approach, open Terminal, type zip -er ~/Desktop/filename.zip (with a space at the end), drag in the files you want to compress, press Return, and enter your desired password when prompted.
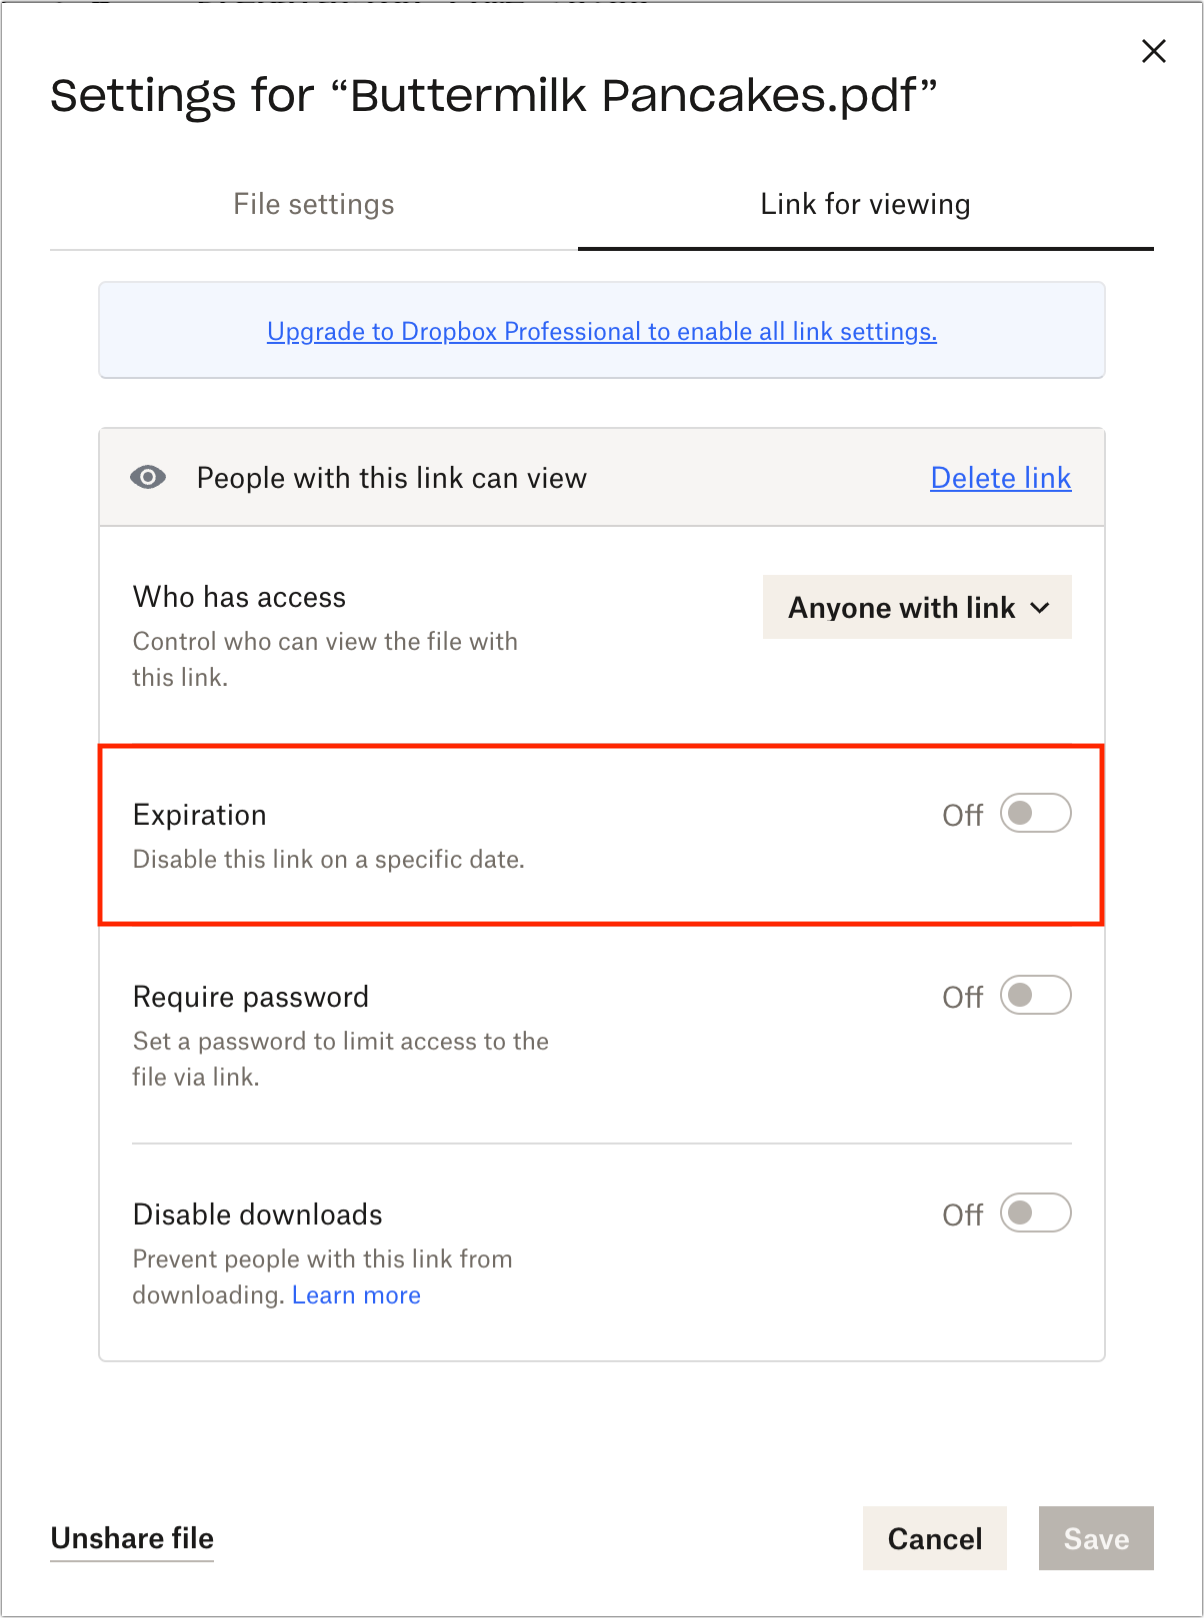
8. Time-expiring cloud storage links: Some cloud storage services offer links that expire after a specified time. Dropbox Professional supports this feature, enabling you to share files while ensuring that links become useless in the event of a breach.
There’s no one-size-fits-all solution for securely sharing sensitive information. Match your approach to the sensitivity of the data, your recipient’s capabilities, and how long they need access.
(Featured image by iStock.com/metamorworks)
Apple Raises Prices on Macs and iPads, but not iPhones or Apple Watches… Yet
Apple just raised Mac and iPad prices by 15–33%, blaming the AI industry’s hunger for memory and storage chips. The iPhone and Apple Watch were spared, but the next new models may be more expensive. Here’s what you need to know.
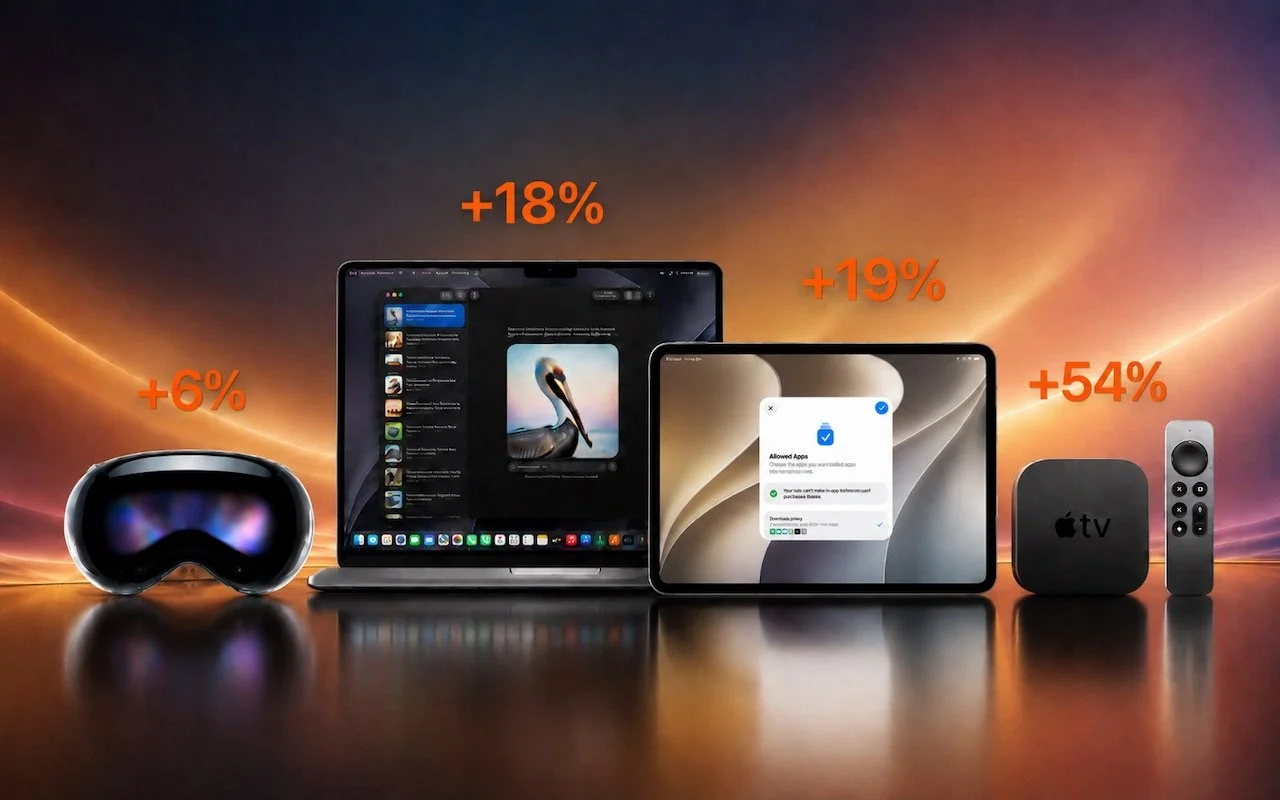
There’s no way to put a positive spin on this: Apple has raised prices across most of its product lineup, with increases averaging 20% on Macs, iPads, HomePods, the Apple TV, and even the Vision Pro. The iPhone and Apple Watch remain unaffected… for now.
The price hikes took effect on June 25. In a statement to the press, Apple blamed the AI industry’s insatiable appetite for memory chips, which has caused prices for memory and storage to increase up to sixfold:
The consumer electronics industry is facing an unprecedented challenge. The rapid expansion of AI data centers has created an extraordinary surge in demand for memory and storage. We have never seen a component price increase this much, this quickly. We have shielded our customers from these increases so far, but we have now reached a point where we need to begin raising prices on a number of products.
Apple’s price increases vary widely. The base model of the Apple TV 4K took the biggest percentage hit, jumping from $129 to $199—a 54% increase that’s particularly puzzling given the device has only 64 GB of storage and 4 GB of memory. It may be setting a new price floor for the next-generation Apple TV. At the other end of the percentage increase spectrum, the Vision Pro rose just 6%, from $3,499 to $3,699.
Mac and iPad Price Changes
The Mac lineup saw significant increases at both the low and high ends:
MacBook Neo: $599 → $699 (+17%)
MacBook Air (13-inch): $1,099 → $1,299 (+18%)
MacBook Pro (14-inch base): $1,699 → $1,999 (+18%)
Mac mini (M4): $599 → $799 (+33%)
Mac Studio (M3 Ultra): $3,999 → $5,299 (+33%)
The $1,300 increase for the M3 Ultra model of the Mac Studio is the largest absolute dollar jump in the lineup—a reflection of just how much high-memory configurations are affected by the shortage.
iPads saw increases of 15–30%, with the base iPad hit hardest:
iPad: $349 → $449 (+29%)
iPad mini: $499 → $599 (+20%)
iPad Air (11-inch): $599 → $749 (+25%)
iPad Air (13-inch): $799 → $949 (+19%)
iPad Pro (11-inch): $999 → $1,199 (+20%)
iPad Pro (13-inch): $1,299 → $1,499 (+15%)
Base prices tell only part of the story. Memory and storage upgrade prices also jumped dramatically, with the 64 GB and 128 GB memory upgrades for M5 Max models of the MacBook Pro doubling in price.
Why iPhones and Apple Watches Were Spared
Apple left the prices for the iPhone, Apple Watch, AirPods, and Studio Display unchanged. The Studio Displays and AirPods likely escaped because they use minimal memory. The iPhone and Apple Watch are a different story—Apple may be willing to accept lower margins on its flagship products, betting that stable prices will drive enough additional sales to offset reduced profit per unit.
There’s also the timing factor. New iPhone and Apple Watch models are expected in September, and rumors suggest Apple will introduce only high-end (and higher margin) iPhone 18 models then, with more affordable models held until early 2027. That makes buying a current-generation iPhone now potentially the better deal—new models will almost certainly debut at higher prices.
Apple Isn’t Alone
The memory crisis has hit the entire consumer electronics industry. Microsoft raised prices on all Surface PCs. Samsung is raising prices on its Galaxy smartphones. Lenovo, HP, and Dell have all raised laptop prices.
The culprit is the industry’s rapid expansion into AI. Data centers are consuming memory and storage at a pace the industry wasn’t equipped to handle. Memory chip suppliers like Micron, Samsung, and SK Hynix have directed production toward AI chipmakers like Nvidia, who are willing to pay top dollar, leaving consumer electronics to compete for whatever remains. Industry observers expect the shortage to persist through at least 2027 due to the time required to build manufacturing capacity.
What Should You Do?
If you need a Mac or iPad, some retailers may not have updated prices yet, but that won’t last. Similarly, you could look for a refurbished Mac from Apple or a certified pre-owned Mac from retailers like OWC, but those prices have largely increased as well.
For the iPhone and Apple Watch, the calculus is unusual: normally, we’d encourage waiting for September’s new models, but this year, buying now at current prices may save you some money.
Ultimately, the only options may be to bite the bullet and pay current prices, buy a less-expensive model or configuration, or hold on to your existing hardware in the hopes that prices come back down.
(Featured image generated by Adam Engst with ChatGPT)
Understanding AI Today: No Longer Just a Chatbot
Still thinking of AI as just a chatbot? Today’s tools search the Web, run code, access your files, and can even take actions—all triggered from the same chat interface. The results are better but come with new responsibilities.
When ChatGPT launched in late 2022, using it was simple: you typed a prompt, and it generated text in response. That text came from a statistical model trained on data available at the time. If you asked ChatGPT about anything that had happened more recently, it either couldn’t help or would confidently make stuff up.
The chat interface that today’s AI systems still rely on has become more of a control panel than the system itself. What happens after you press Return may involve Web searches, file analysis, code execution, connected accounts, and even digital-world actions—all orchestrated behind the scenes. You need to understand what’s happening behind the chat box to evaluate the accuracy, quality, and utility of the answers that appear there.
Under the Hood of an AI System
The capabilities of a modern AI system include:
Models generate text, analyze images, and work through problems. This is the traditional “AI” part, but it has improved hugely through better training techniques, longer conversations and documents, and extended reasoning time. Cutoff dates for training models remain an issue—some AIs think macOS 26 is still in beta.
Retrieval pulls information from the Web, uploaded documents, or connected data sources. When an AI cites a source, it’s usually because retrieval happened. However, it’s still essential to check cited sources carefully because the URLs may be broken, and even when pages exist, they may not support the claims.
Tools handle tasks the model can’t do on its own, such as analyzing numeric data, running code, creating visualizations, or searching databases. For many types of requests, the AI will write a script or call a tool to handle the work, dramatically increasing the likelihood that the results will be correct and making it easier to refine them.
Connectors link AI systems to external platforms such as email, calendars, file storage, and Internet-hosted applications. They’re necessary so a system can work on personalized data (“Give me a timeline of the deliverables on the MacDavis project from our email conversations.”) and to connect with business data.
Actions let AI systems do things in the digital world: send messages, create events, modify files, and interact with other software. Here is where AI stops merely advising and starts affecting real systems, so the safeguards need to be much stronger.
These capabilities don’t always appear together. A simple chatbot exchange may rely only on the model’s training. A research request may add retrieval and tools so the AI can search current sources, summarize what it finds, and run calculations or create charts. A workplace copilot may add connectors to email, calendars, cloud storage, customer records, or internal databases. A full-fledged agent adds actions, enabling the system to operate on your behalf.
It’s important to understand all the possibilities because each layer changes both what the AI can do and how much you should trust it. A model-only answer calls for skepticism (and perhaps a search). A search-based answer needs source checking. A tool-generated answer requires checking the inputs, method, and results. A connector-based answer warrants attention to the source of the data (and whether the permissions are too broad). And an action deserves a preview, an approval process, and ideally a way to undo mistakes.
What This Means for Trust, Privacy, and Control
This evolution from chatbot to assistant generally yields better results, but it also comes with new risks:
Privacy isn’t just about what you type. It’s about what files you upload, what accounts you connect, and what the AI system can access. Putting confidential data into an AI could be problematic in numerous ways, not least regulatory compliance.
Accuracy varies by task. Responses drawn purely from training data may be outdated or flat-out wrong, while search-informed answers reflect current sources. Asking an AI to “Confirm with a search” is a good way to get it to reassess what it has written with current information.
Actions have consequences. When AI can send email, modify files, change settings, or interact with business systems, mistakes can have outsized impacts. This is why we strongly recommend caution about OpenClaw-style agents: giving any AI broad access to email, messaging, calendars, files, and applications creates security and reliability risks. Always preview any action—or AI-generated script you’re running externally—whose results could be difficult or impossible to reverse.
Confidence isn’t correctness. AI outputs can sound polished and authoritative even when they contain errors, outdated information, or subtle misunderstandings of your intent. Any AI-generated work that informs decisions or will be seen by others deserves human review. Just as you wouldn’t base anything important on the work of a summer intern without checking first, you don’t want AI-generated work to go out if you can’t stand behind it.
For individuals, how you react to these risks mostly comes down to verification and restraint: check important sources, review important outputs, and don’t let AI take irreversible actions without approval. For organizations, the same principles must become policy because employees may already be using AI tools with company data without IT’s knowledge. To get ahead of the issue, organizations should:
Audit what’s already happening. Talk with employees to find out what they’re already using, inventory online apps with embedded AI features, and check browser extensions, which often fly under the radar.
Classify workflows by risk. Not all workflows need the same level of attention. Low-stakes tasks like brainstorming and text editing can proceed with commonsense guidelines. High-stakes outputs—client communications, financial analysis, security configurations—need human review before they go live.
Evaluate tools carefully. Before approving any AI tool for general use, understand what data it accesses, whether it trains on your inputs, what actions it can take, and what logging is available. Most paid tools won’t train on your data, or can at least be configured not to, but the more important your data, the deeper your research should go.
Create clear policies and train employees. Define which tools are approved, what data can be entered into AI systems, when human review is required, and what’s prohibited. Employees need practical guidance on how to apply the policies to their actual workflows. Don’t assume that an email or two is sufficient—training is essential.
The biggest mistake people make about AI today is underestimating both its risks and rewards because they’re still thinking about ChatGPT from 2023. The chat box may look the same, but it now sits in front of systems that are vastly more powerful, meaning that it’s more important than ever to consider when to trust them, when to verify them, and when to keep them at arm’s length.
(Featured image by iStock.com/tadamichi)
Choosing the Best Mac for a College-Bound Student in 2026
Which Mac is best for a college student now? The 13-inch or 15-inch M5 MacBook Air hits the sweet spot of performance, portability, and price. If budget is a constraint, consider the MacBook Neo; for more power, choose the 14-inch MacBook Pro.
If you have a college-bound student, it’s time to think about whether they need a new Mac. Perhaps their current computer is showing its age, or it was a high school loaner, or it would be better handed down to a younger sibling. Whatever the reason, navigating Apple’s current Mac lineup can feel overwhelming, especially given the wide range of price points. Here’s how to choose.
First, you (or your child) will need to do some homework. Check with the college for any technical requirements. Some programs or majors mandate specific processor types, memory amounts, or storage capacities based on the software their students use. Current Macs can usually meet or exceed these specs without issue. A more pressing concern is whether a particular field of study requires Windows. If so, dig deeper—is the requirement driven by specific Windows-only software, or is it simply the IT department’s preference for a uniform support environment? It’s also worth checking if the college offers educational pricing. Most do, and you can usually save a few hundred dollars. Apple also typically runs a Back to School promotion that may be interesting.
For college students, a laptop makes far more sense than a desktop Mac. Students rarely stay put—they work in lecture halls, libraries, the quad, coffee shops, and wherever they can find a seat. There’s also the matter of breaks: when students head home, they need a computer that travels with them so they can keep working on assignments. A student who’s already comfortable taking notes on an iPad with a keyboard and Apple Pencil could potentially supplement that with a desktop Mac, but for the vast majority, a laptop is best.
Apple’s MacBook Choices
Happily, Apple’s current lineup offers something for nearly every student. We see four primary scenarios:
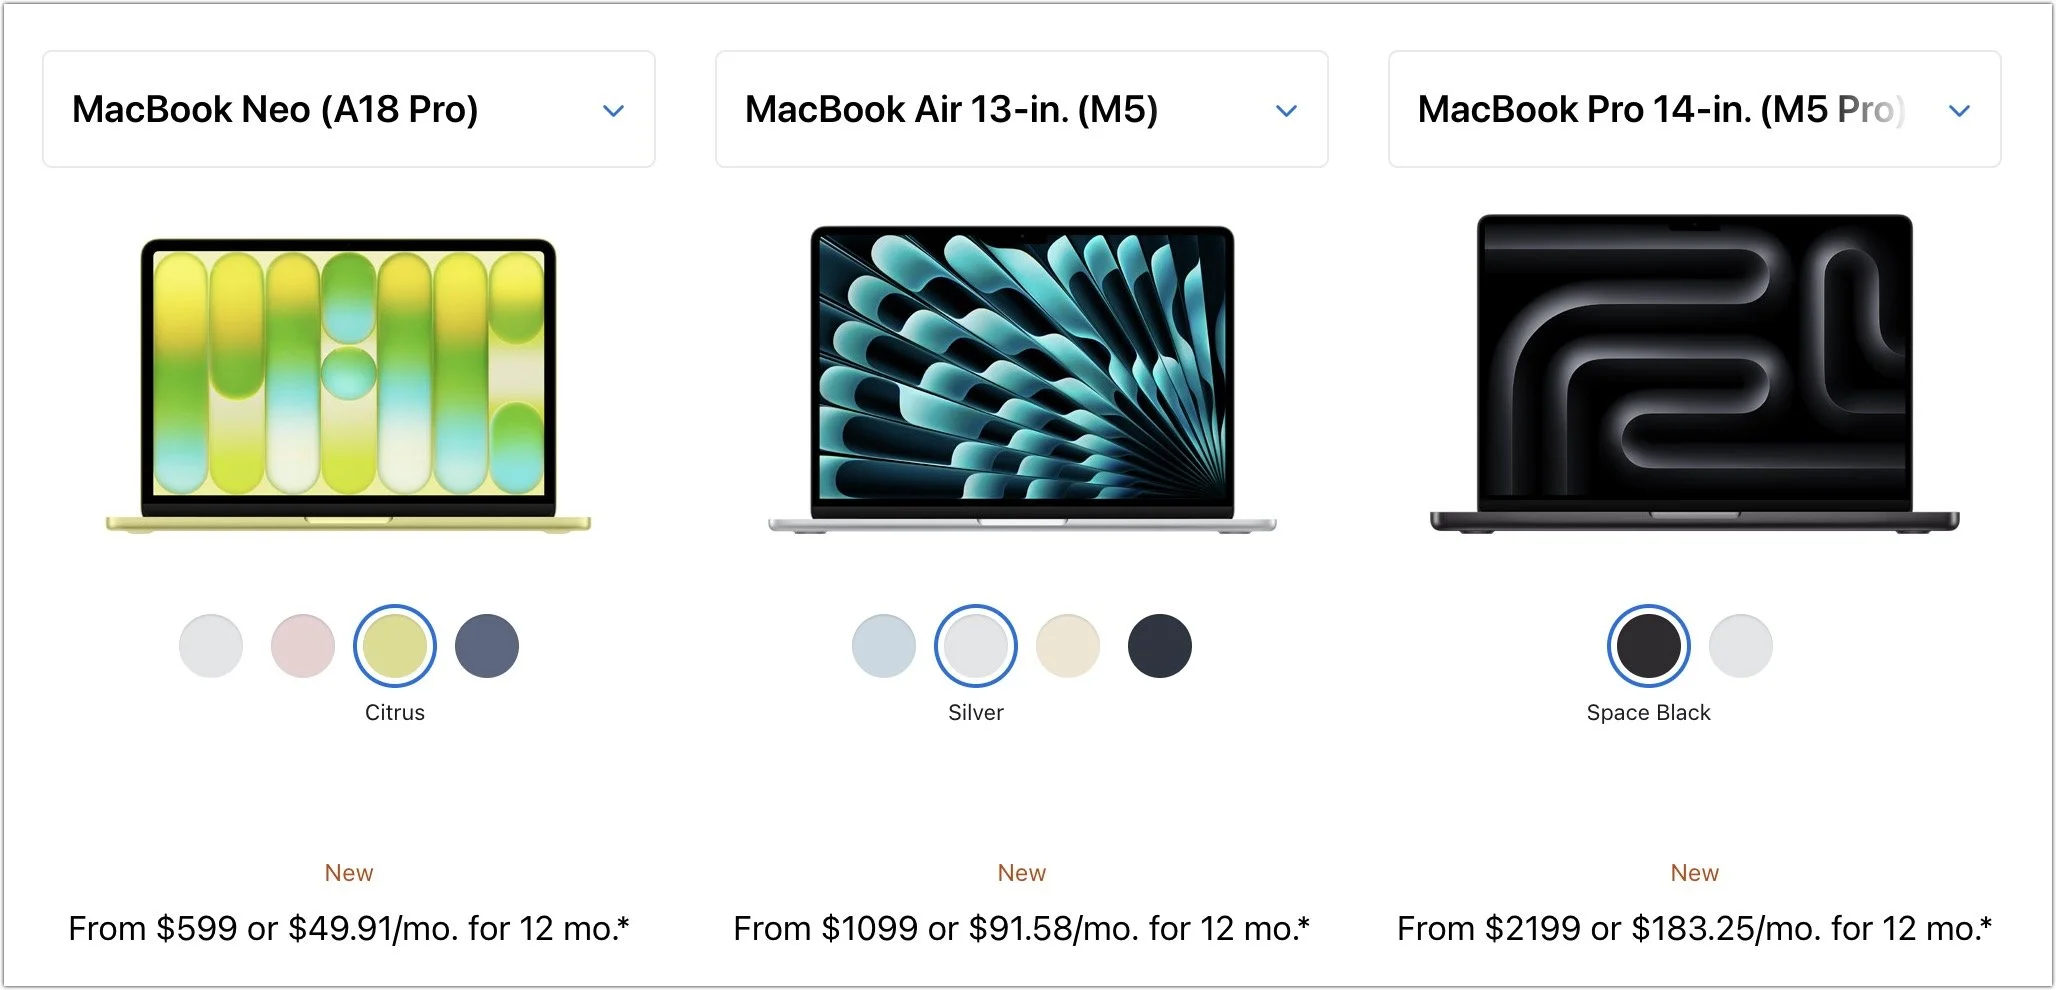
Most students: Buy Apple’s MacBook Air, the company’s most popular laptop. The 13-inch and 15-inch M5 MacBook Air models, refreshed in March 2026, now start with 512 GB of storage and feature faster SSDs. The 13-inch M5 MacBook Air features a 13.6-inch screen, a memory ceiling of 32 GB, and up to 4 TB of storage, starting at $1,099. For those who want a larger display, the 15-inch M5 MacBook Air is a great choice, starting at $1,299. Otherwise, it’s nearly identical to its smaller sibling.
Better specs: If performance is more important than price, consider the 14-inch MacBook Pro. It features M5, M5 Pro, or M5 Max chips. The entry-level M5 model starts at $1,699, but there’s little reason to choose it over the M5 MacBook Air. For students who need more power, the M5 Pro ($2,199) and M5 Max ($3,599) can be configured with significantly more memory—up to 64 GB with the M5 Pro or 128 GB with the M5 Max. Students majoring in film production, computer science with a focus on machine learning, or other fields involving heavy computation may benefit from an M5 Pro and more memory. (There’s also a 16-inch MacBook Pro in M5 Pro and M5 Max configurations—the larger screen is nice for video work, but it’s heavy and way more expensive.)
Budget choice: If budget is the primary constraint, look at Apple’s new $599 MacBook Neo. It handles basic tasks like Web browsing, writing papers, and video streaming without issue. However, it has significant limitations: only 8 GB of memory, an iPhone-class A18 Pro chip that’s notably slower than the M5, and a limited port selection. The Neo is adequate for students whose coursework involves only word processing, Web research, and light productivity apps—but it won’t suffice for students who discover a passion for video editing, data analysis, or 3D modeling.
Windows compatibility: The only downside of Macs with Apple silicon is that it’s more challenging to run Windows using virtualization software like Parallels Desktop (available at half price for students) or VMware Fusion (free for personal use). If Windows is a bonus but not essential, Windows 11 for Arm should work for most apps. However, if Windows compatibility and performance are crucial, your best option is—much as we hate to say it—a PC laptop.
Choosing Processor, Memory, and Storage Options
No matter which laptop you choose, you’ll need to select a processor, memory size, and storage capacity:
Processor: For the most part, processor choice tracks with model and budget. The low-end MacBook Neo only offers an A18 Pro with a 6-core CPU and 5-core GPU. The mid-range MacBook Air models have an M5 with a 10-core CPU and either an 8-core or 10-core GPU; the extra GPU cores offer a little more performance for an extra $100. The powerful 14-inch MacBook Pro offers a choice between the M5 and multiple configurations of the M5 Pro and M5 Max. The base M5 model performs the same as the M5 MacBook Air, but students with significant computational needs will benefit from an M5 Pro or M5 Max, with price being the main constraint.
Memory: The MacBook Neo has 8 GB of memory with no upgrade option—sufficient for basic tasks but limiting for demanding apps or heavy multitasking. The M5 MacBook Air models start at 16 GB and offer 24 or 32 GB options. On the 14-inch MacBook Pro, memory capacity varies by chip. The M5 Pro comes standard with 24 GB, with upgrade options to 48 or 64 GB. The M5 Max has a standard memory spec of 36 GB, with upgrade options to 48, 64, or 128 GB. Students can typically stick with 16 GB or choose 24 GB for more demanding tasks—a few will require 32 GB or more.
Storage: The MacBook Neo starts at 256 GB ($599) or 512 GB ($699, which also adds Touch ID, a welcome feature for a college student using their laptop in public spaces). For both MacBook Air models, 512 GB is the minimum storage option, with upgrades up to 4 TB. The 14-inch MacBook Pro with M5 Pro starts at 1 TB, while M5 Max models start at 2 TB, with upgrades up to 8 TB. Choose the storage capacity based on two factors: budget (storage gets expensive quickly) and anticipated usage (audio and particularly video production can consume a lot of space, as can large numbers of images). It’s easy to offload large, infrequently used files to an external SSD or hard drive, but external storage prices have skyrocketed lately, making Apple’s prices for internal storage less extreme.
Our Recommendation
For most students, the best choice for a Mac likely to last four years of college is the 13-inch or 15-inch M5 MacBook Air, equipped with 16 GB or 24 GB of memory and either 512 GB or 1 TB of storage. While the 15-inch model has a larger screen, it’s heavier and takes up more space in a backpack, so consider portability when making your final decision. Be sure to budget for AppleCare+ as well; it’s almost certain that a mishap will occur with a student laptop, and AppleCare+ covers up to two incidents of accidental damage per year.
Be sure to talk with your child to learn more about what they think they’ll need—and compare it to the college’s recommendations—but if you have any questions afterward, feel free to reach out to us.
(Featured image by iStock.com/Zbynek Pospisil)